


Author: admin
ZDI-25-413: Fuji Electric Smart Editor TL5 File Parsing Stack-Based Buffer Overflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Fuji Electric Smart Editor. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-41388.
ZDI-25-412: Fuji Electric Smart Editor X1 File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Fuji Electric Smart Editor. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-41413.
ZDI-25-411: Delta Electronics CNCSoft-G2 DPAX File Parsing Memory Corruption Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Delta Electronics CNCSoft-G2. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-47728.
Extracting Embedded MultiMediaCard (eMMC) contents in-system
Every complex modern device needs non-volatile storage to keep program and configuration data while unpowered. There are several competing options on the market available to today’s systems designers: serial Flash, raw NAND chips, (micro)SD, and Embedded MultiMediaCard (eMMC). eMMC is the topic of this discussion, and specifically how to interact with it without removing the …
Extracting Embedded MultiMediaCard (eMMC) contents in-systemRead More
ZDI-25-410: Allegra calculateTokenExpDate Password Recovery Authentication Bypass Vulnerability
This vulnerability allows remote attackers to bypass authentication on affected installations of Allegra. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2025-6216.
ZDI-25-409: RARLAB WinRAR Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of RARLAB WinRAR. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-6218.
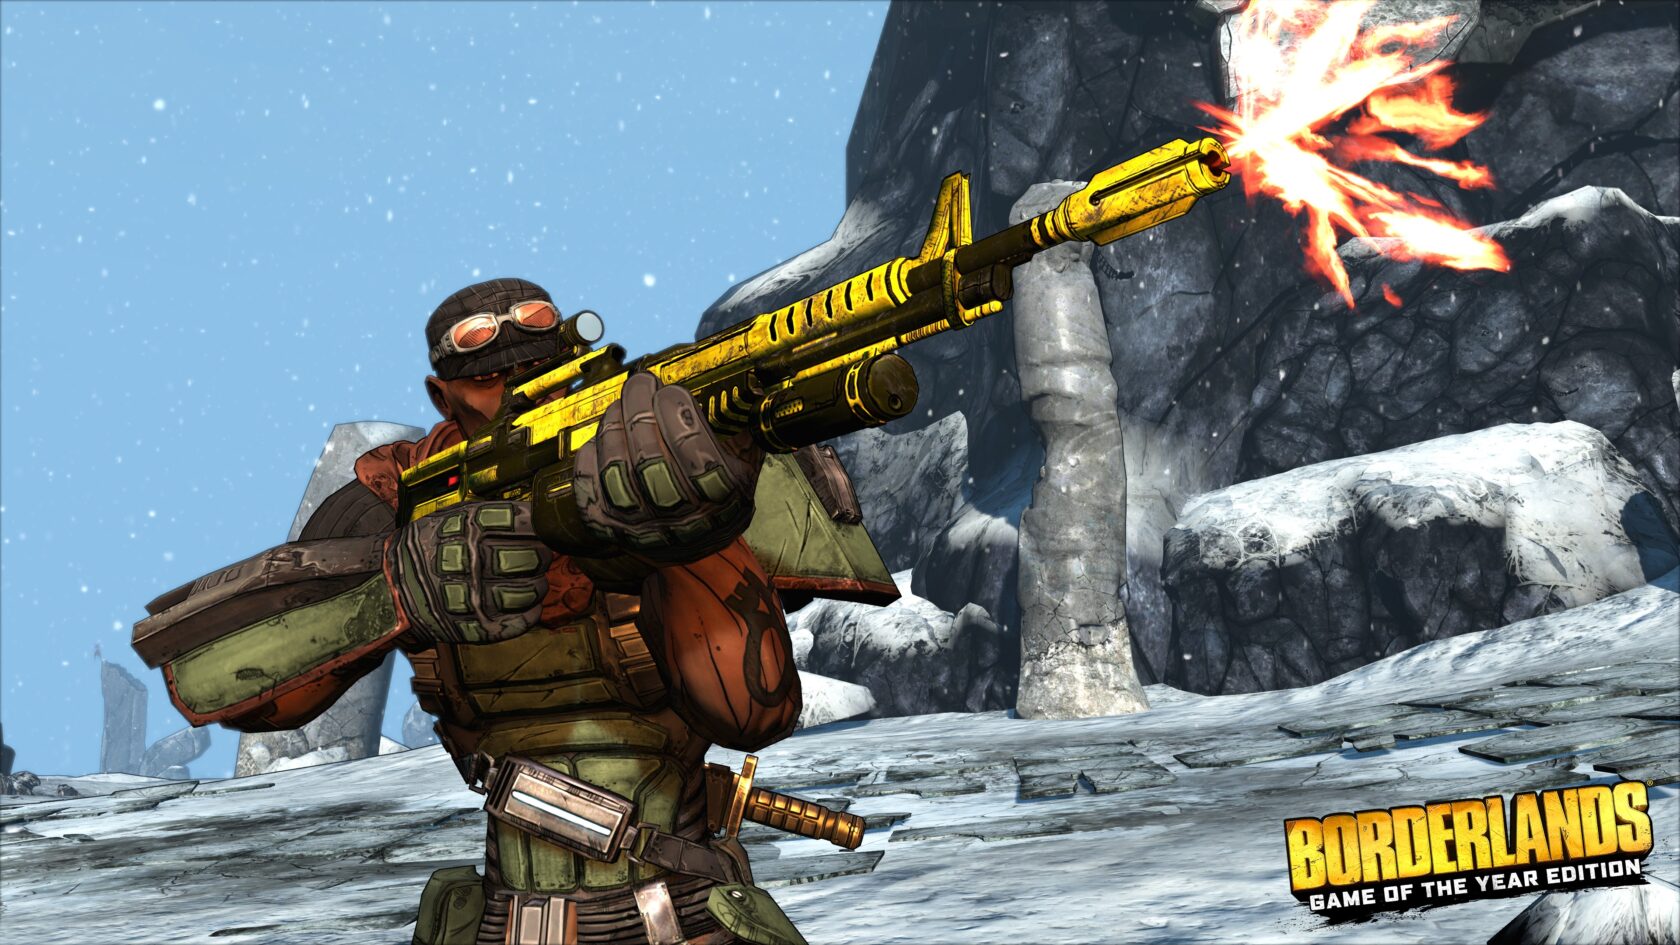
Step Inside the Vault: The ‘Borderland’ Series Arrives on GeForce NOW
GeForce NOW is throwing open the vault doors to welcome the legendary Borderland series to the cloud. Whether a seasoned Vault Hunter or new to the mayhem of Pandora, prepare to experience the high-octane action and humor that define the series that includes Borderlands Game of the Year Enhanced, Borderlands 2, Borderlands 3 and Borderlands: …
Step Inside the Vault: The ‘Borderland’ Series Arrives on GeForce NOWRead More
ZDI-25-408: PEAK-System Driver PCANFD_ADD_FILTERS Time-Of-Check Time-Of-Use Information Disclosure Vulnerability
This vulnerability allows local attackers to disclose sensitive information on affected installations of PEAK-System Driver. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 3.8. The following CVEs are assigned: CVE-2025-6217.
Plug and Play: Build a G-Assist Plug-In Today
Project G-Assist — available through the NVIDIA App — is an experimental AI assistant that helps tune, control and optimize NVIDIA GeForce RTX systems. NVIDIA’s Plug and Play: Project G-Assist Plug-In Hackathon — running virtually through Wednesday, July 16 — invites the community to explore AI and build custom G-Assist plug-ins for a chance to …
ZDI-25-407: SolarWinds Web Help Desk AjaxProxy Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of SolarWinds Web Help Desk. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2024-28988.






