


Month: April 2025
How Agentic AI Enables the Next Leap in Cybersecurity
Agentic AI is redefining the cybersecurity landscape — introducing new opportunities that demand rethinking how to secure AI while offering the keys to addressing those challenges. Unlike standard AI systems, AI agents can take autonomous actions — interacting with tools, environments, other agents and sensitive data. This provides new opportunities for defenders but also introduces …
How Agentic AI Enables the Next Leap in CybersecurityRead More
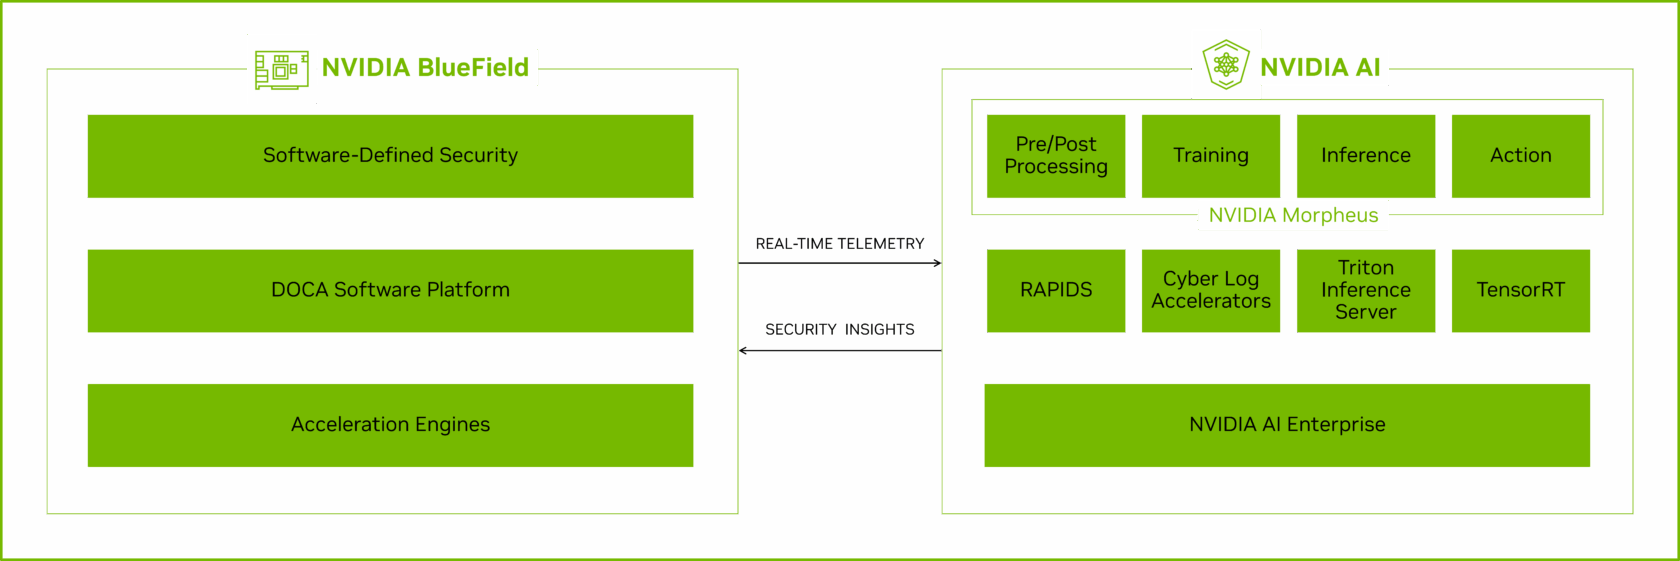
NVIDIA Brings Cybersecurity to Every AI Factory
As enterprises increasingly adopt AI, securing AI factories — where complex, agentic workflows are executed — has never been more critical. NVIDIA is bringing runtime cybersecurity to every AI factory with a new NVIDIA DOCA software framework, part of the NVIDIA cybersecurity AI platform. Running on the NVIDIA BlueField networking platform, NVIDIA DOCA Argus operates …
ZDI-25-256: Avast Free Antivirus Integer Overflow Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Avast Free Antivirus. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2025-3500.
ZDI-25-255: Allegra isZipEntryValide Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Allegra. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2025-3486.
ZDI-25-254: Allegra extractFileFromZip Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Allegra. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2025-3485.
ZDI-25-253: SonicWALL Connect Tunnel Link Following Denial-of-Service Vulnerability
This vulnerability allows local attackers to create a denial-of-service condition on affected installations of SonicWALL Connect Tunnel. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 6.1. The following CVEs are assigned: CVE-2025-32817.
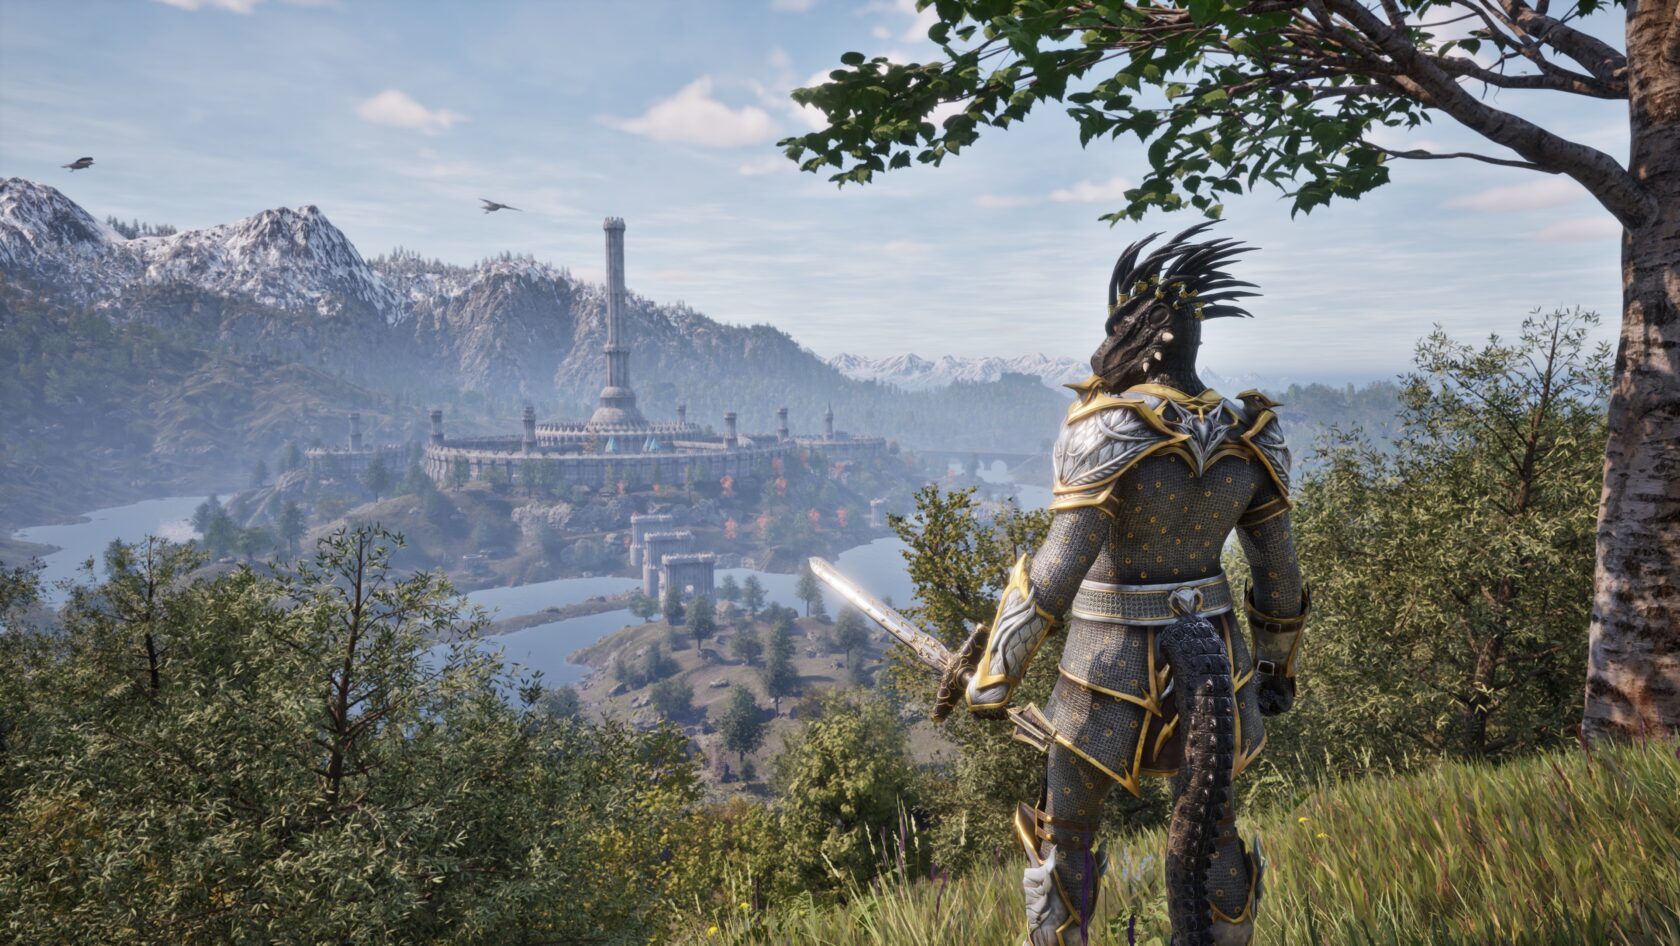
All Roads Lead Back to Oblivion: Bethesda’s ‘The Elder Scrolls IV: Oblivion Remastered’ Arrives on GeForce NOW
Get the controllers ready and clear the calendar — it’s a jam-packed GFN Thursday. Time to revisit a timeless classic for a dose of remastered nostalgia. GeForce NOW is bringing members a surprise from Bethesda — The Elder Scrolls IV: Oblivion Remastered is now available in the cloud. Clair Obscur: Expedition 33, the spellbinding turn-based …
NVIDIA Research at ICLR — Pioneering the Next Wave of Multimodal Generative AI
Advancing AI requires a full-stack approach, with a powerful foundation of computing infrastructure — including accelerated processors and networking technologies — connected to optimized compilers, algorithms and applications. NVIDIA Research is innovating across this spectrum, supporting virtually every industry in the process. At this week’s International Conference on Learning Representations (ICLR), taking place April 24-28 …
NVIDIA Research at ICLR — Pioneering the Next Wave of Multimodal Generative AIRead More
ZDI-25-252: (0Day) Cato Networks Cato Client for macOS Helper Service Time-Of-Check Time-Of-Use Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Cato Networks Cato Client for macOS. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-3886.
ZDI-25-251: (0Day) Harman Becker MGU21 Bluetooth Improper Input Validation Denial-of-Service Vulnerability
This vulnerability allows network-adjacent attackers to create a denial-of-service condition on affected installations of Harman Becker MGU21 devices. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 5.3. The following CVEs are assigned: CVE-2025-3885.






