


Month: March 2025
MindshaRE: Using Binary Ninja API to Detect Potential Use-After-Free Vulnerabilities
Use-after-free is a memory corruption condition where a program references memory after it has been released back to the allocator. Statically detecting these bugs can be challenging. In the past, several approaches have addressed this problem, such as GUEB by Josselin Feist and Sean Heelan’s work on Finding use-after-free bugs with static analysis. This blog …
MindshaRE: Using Binary Ninja API to Detect Potential Use-After-Free VulnerabilitiesRead More
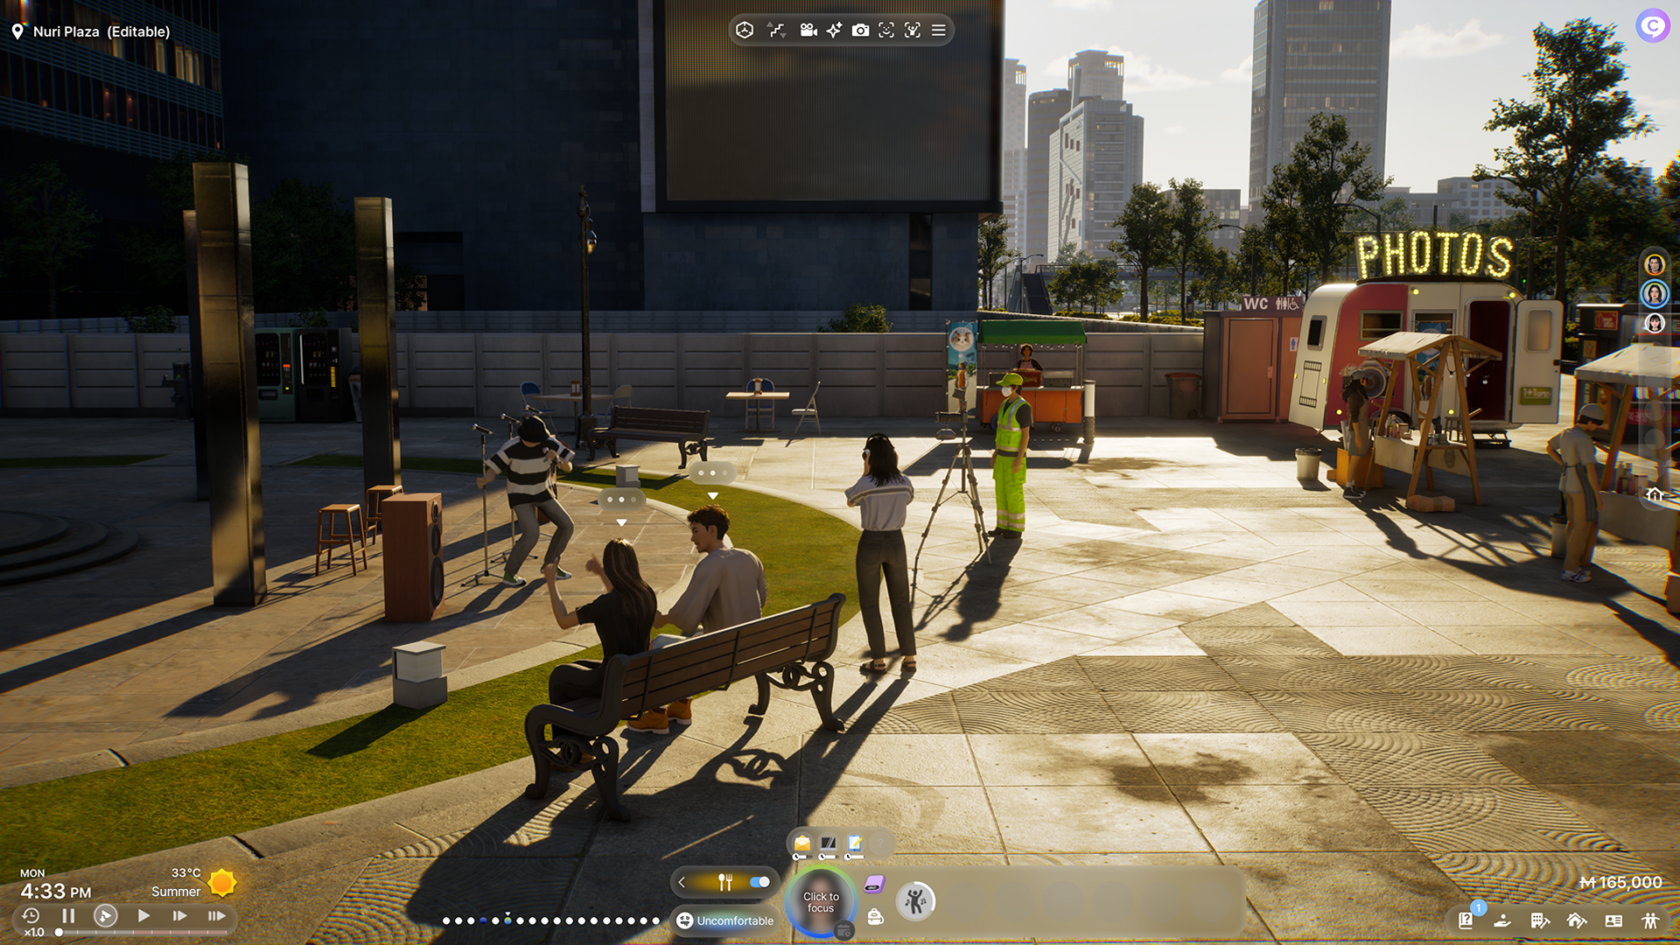
The Dream Life Awaits: Play ‘inZOI’ on GeForce NOW Anytime, Anywhere
A new resident is moving into the cloud — KRAFTON’s inZOI joins the 2,000+ games in the GeForce NOW cloud gaming library. Plus, members can get ready for an exclusive sneak peek as the Sunderfolk First Look Demo comes to the cloud. The demo is exclusively available for players on GeForce NOW until April 7, …
The Dream Life Awaits: Play ‘inZOI’ on GeForce NOW Anytime, AnywhereRead More
Buzz Solutions Uses Vision AI to Supercharge the Electric Grid
The reliability of the electric grid is critical. From handling demand surges and evolving power needs to preventing infrastructure failures that can cause wildfires, utility companies have a lot to keep tabs on. Buzz Solutions — a member of the NVIDIA Inception program for cutting-edge startups — is helping by using AI to improve how …
Buzz Solutions Uses Vision AI to Supercharge the Electric GridRead More
ZDI-25-187: (0Day) BEC Technologies Multiple Routers sys ping Command Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of BEC Technologies Multiple Routers. Although authentication is required to exploit this vulnerability, the existing authentication mechanism can be bypassed. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2025-2773.
ZDI-25-186: (0Day) BEC Technologies Multiple Routers Cleartext Password Storage Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of BEC Technologies routers. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 4.9. The following CVEs are assigned: CVE-2025-2770.
ZDI-25-185: (0Day) BEC Technologies Multiple Routers Insufficiently Protected Credentials Information Disclosure Vulnerability
This vulnerability allows network-adjacent attackers to disclose sensitive information on affected installations of BEC Technologies routers. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 5.3. The following CVEs are assigned: CVE-2025-2772.
ZDI-25-184: (0Day) BEC Technologies Multiple Routers Authentication Bypass Vulnerability
This vulnerability allows remote attackers to bypass authentication on affected installations of BEC Technologies routers. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 5.3. The following CVEs are assigned: CVE-2025-2771.
ZDI-25-175: (0Day) Luxion KeyShot USDC File Parsing Use-After-Free Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Luxion KeyShot. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-2532.
ZDI-25-174: (0Day) Luxion KeyShot DAE File Parsing Heap-based Buffer Overflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Luxion KeyShot. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-2531.
ZDI-25-173: (0Day) Luxion KeyShot DAE File Parsing Access of Uninitialized Pointer Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Luxion KeyShot. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-2530.






