


Author: admin
ZDI-25-446: PDF-XChange Editor App Object Use-After-Free Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of PDF-XChange Editor. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-6661.
ZDI-25-445: PDF-XChange Editor PRC File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of PDF-XChange Editor. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-6659.
ZDI-25-444: PDF-XChange Editor PRC File Parsing Out-Of-Bounds Read Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of PDF-XChange Editor. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 3.3. The following CVEs are assigned: CVE-2025-6658.
ZDI-25-418: Apple macOS CoreGraphics PDF File Parsing Out-Of-Bounds Read Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Apple macOS. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 4.3. The following CVEs are assigned: CVE-2025-31196.
HPE and NVIDIA Debut AI Factory Stack to Power Next Industrial Shift
To speed up AI adoption across industries, HPE and NVIDIA today launched new AI factory offerings at HPE Discover in Las Vegas. The new lineup includes everything from modular AI factory infrastructure and HPE’s AI-ready RTX PRO Servers (HPE ProLiant Compute DL380a Gen12), to the next generation of HPE’s turnkey AI platform, HPE Private Cloud …
HPE and NVIDIA Debut AI Factory Stack to Power Next Industrial ShiftRead More
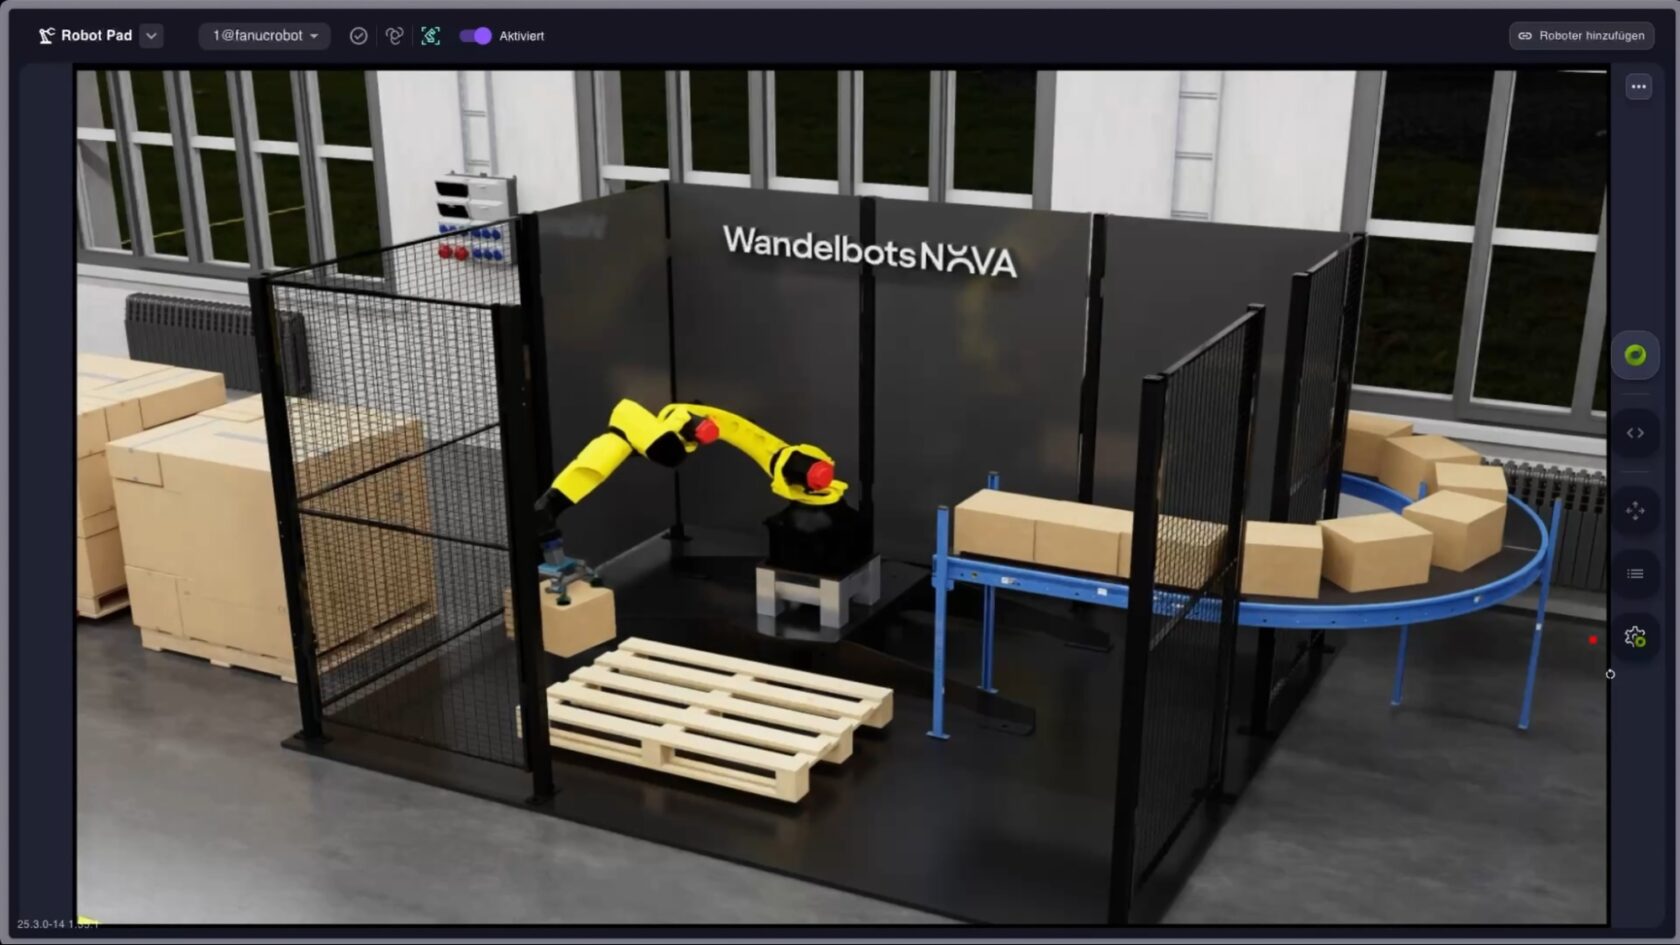
NVIDIA and Partners Highlight Next-Generation Robotics, Automation and AI Technologies at Automatica
From the heart of Germany’s automotive sector to manufacturing hubs across France and Italy, Europe is embracing industrial AI and advanced AI-powered robotics to address labor shortages, boost productivity and fuel sustainable economic growth. Robotics companies are developing humanoid robots and collaborative systems that integrate AI into real-world manufacturing applications. Supported by a $200 billion …
ZDI-25-417: Clam AntiVirus UDF File Parsing Out-Of-Bounds Read Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Clam AntiVirus. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 6.1. The following CVEs are assigned: CVE-2025-20234.
ZDI-25-416: ServiceStack FindType Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of ServiceStack. Interaction with this library is required to exploit this vulnerability but attack vectors may vary depending on the implementation. The ZDI has assigned a CVSS rating of 8.1. The following CVEs are assigned: CVE-2025-6445.
ZDI-25-415: ServiceStack GetErrorResponse Improper Input Validation NTLM Relay Vulnerability
This vulnerability allows remote attackers to relay NTLM credentials on affected installations of ServiceStack. Interaction with this library is required to exploit this vulnerability but attack vectors may vary depending on the implementation. The ZDI has assigned a CVSS rating of 5.9. The following CVEs are assigned: CVE-2025-6444.
ZDI-25-414: Ruby WEBrick read_header HTTP Request Smuggling Vulnerability
This vulnerability allows remote attackers to smuggle arbitrary HTTP requests on affected installations of Ruby WEBrick. This issue is exploitable when the product is deployed behind an HTTP proxy that fulfills specific conditions. The ZDI has assigned a CVSS rating of 6.5. The following CVEs are assigned: CVE-2025-6442.






