


Welcome to Day One of Pwn2Own Berlin 2026! Today, 22 entries took the Pwn2Own stage to target AI Databases, Coding Agents, Local Inferences, and a separate category for NVIDIA products, as the world’s top security researchers push technology to its limits. Exploits, surprises, and breakthrough discoveries are unfolding.
After Day One, we awarded $523,000 for 24 unique 0-days! DEVCORE is currently in the lead for Master of Pwn, but a pack of teams are right on their heels. Stay tuned tomorrow for more results and surprises.
Follow the action live! We’ll be posting real-time updates and results throughout the competition on our blog and across social media. Stay up to date by following us on Twitter, Mastodon, LinkedIn, and Bluesky, and join the conversation using #Pwn2Own Berlin and #P2OBerlin for continuous coverage.

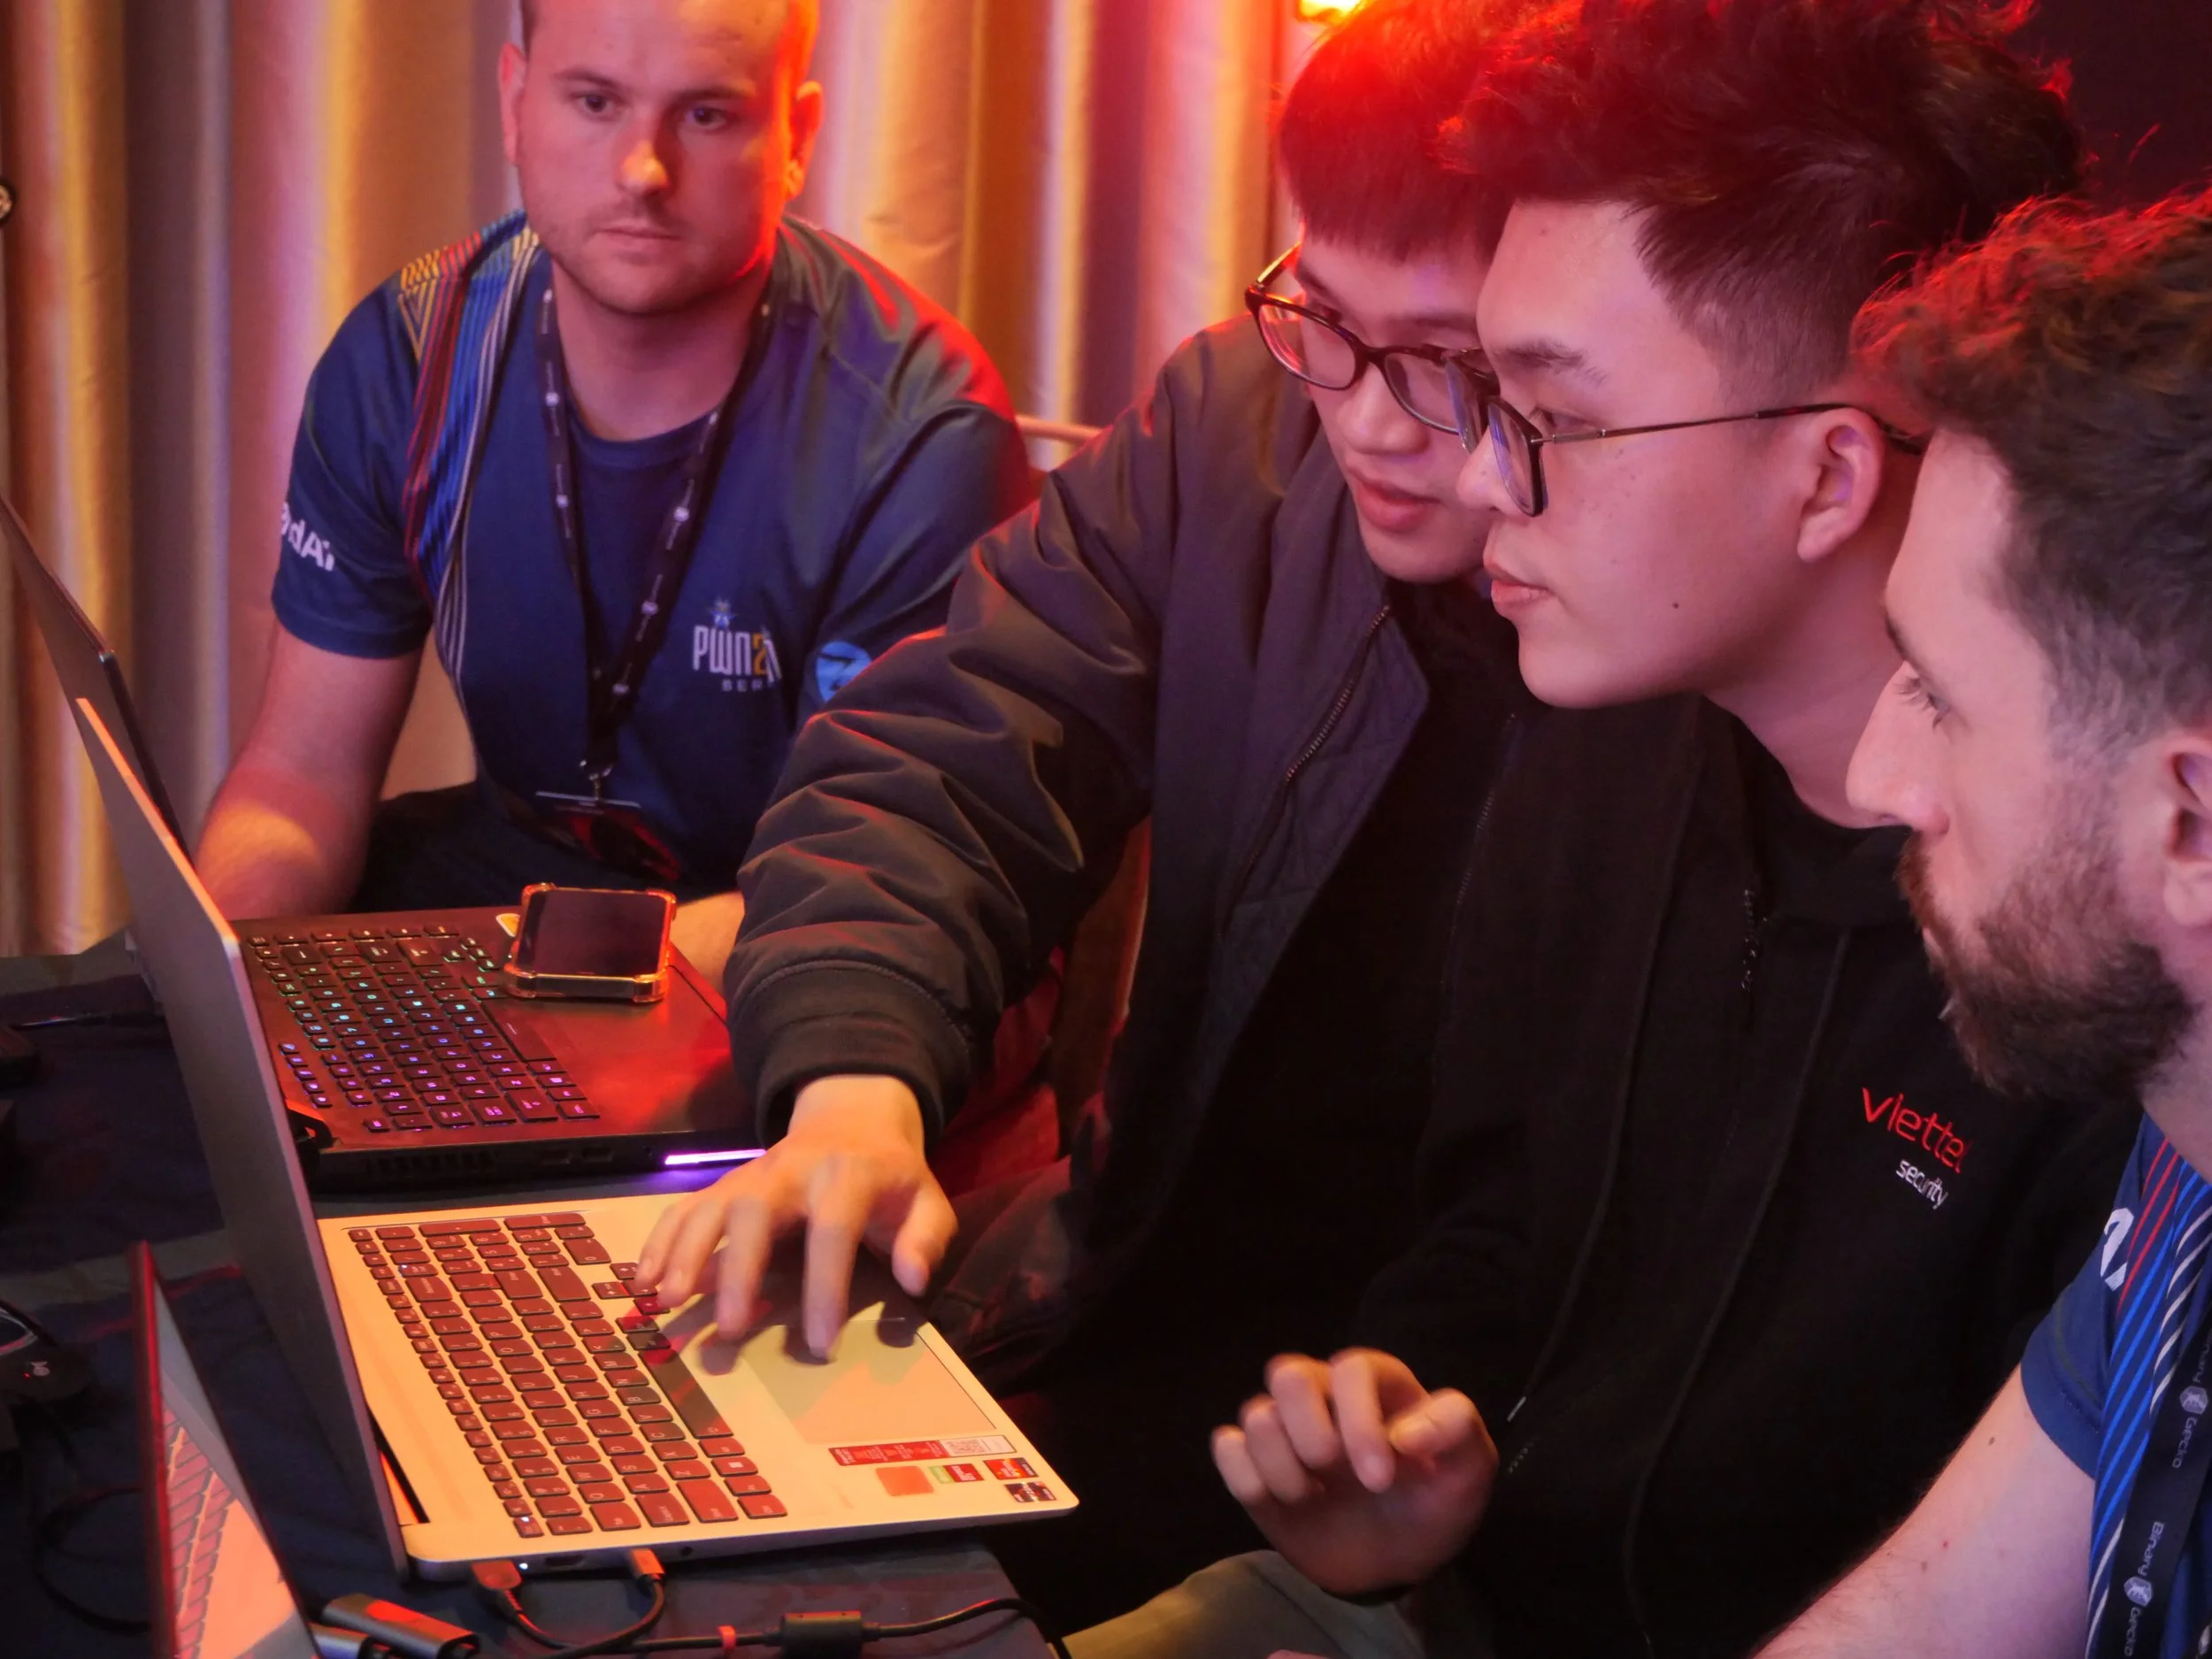
FAILURE – Unfortunately, Le Duc Anh Vu of Viettel Cyber Security could not get their exploit of OpenAI Codex working within the time allotted.
SUCCESS – Orange Tsai (@orange_8361) of DEVCORE Research Team (@d3vc0r3) chained 4 logic bugs to achieve a sandbox escape on Microsoft Edge, earning $175,000 and 17.5 Master of Pwn points.

SUCCESS – chompie of IBM X-Force Offensive Research (XOR) used a single bug to exploit NV Container Toolkit, earning $50,000 and 5 Master of Pwn points.

SUCCESS – k3vg3n chained 3 bugs including SSRF and Code Injection to take down LiteLLM. $40,000 and 4 Master of Pwn points. Full win.

SUCCESS – Satoki Tsuji (@satoki00) of Ikotas Labs, Inc. used an Overly Permissive Allowed List bug to exploit NVIDIA Megatron Bridge, earning $20,000 and 2 Master of Pwn points.

FAILURE – Unfortunately, Park Jae Min could not get their exploit of Oracle Autonomous AI Database working within the time allotted. #Pwn2Own #P2OBerlin
SUCCESS – Emanuele Barbeno, Cyrill Bannwart, Yves Bieri, Lukasz D., Urs Mueller of Compass Security (@compasssecurity) used a single CWE-150 bug to exploit OpenAI Codex, earning $40,000 and 4 Master of Pwn points.
SUCCESS – Angelboy (@scwuaptx) & TwinkleStar03 (@_twinklestar03) of DEVCORE Research Team used an Improper Access Control bug to escalate privileges on Microsoft Windows 11, earning $30,000 and 3 Master of Pwn points.

WITHDRAWAL – Ben Koo (@kiddo_pwn) of Team DDOS has withdrawn their entry for Mozilla Firefox – Renderer Only in the Web Browser category
FAILURE – Unfortunately, Interrupt Labs could not get their exploit of NV Container Toolkit working within the time allotted
COLLISON – Although successful on stage, the Ikotas Labs, Inc. team targeting LiteLLM in the Local Inference category used bugs that were previously known. They still earn $8,000 and 1.75 Master of Pwn points.
SUCCESS – Yoseop Kim (@pwning_me) used a CWE-470 bug to exploit NVIDIA Megatron Bridge in the second round, earning $10,000 and 2 Master of Pwn points.

COLLISON – Although successful on stage, maitai (@MaitaiThe) of Doyensec (@Doyensec) targeting OpenAI Codex in the Coding Agent category used a bug that was previously known to the vendor. They still earn $10,000 and 2 Master of Pwn points.
WITHDRAWAL – Yoseop Kim(@pwning_me) has withdrawn their entry for Mozilla Firefox – Renderer Only in the Web Browser category
SUCCESS – haehae (@haehaeYang) of Out Of Bounds chained 2 bugs (CWE-190, CWE-362) to exploit Chroma, earning $20,000 and 2 Master of Pwn points.


SUCCESS – Billy (@st424204), Pan Zhenpeng (@Peterpan980927) & Weiming Shi (@bestswngs) of STARLabs SG (@starlabs_sg) chained 5 bugs (incl. SSRF and Code Injection) to exploit LM Studio, earning $40,000 and 4 Master of Pwn points. Full win!

SUCCESS – Marcin Wiązowski used a heap-based buffer overflow to escalate privileges on Microsoft Windows 11 in the second round, earning $15,000 and 3 Master of Pwn points.

WITHDRAWAL – Qrious Secure (@qriousec) has withdrawn their entry for LM Studio in the Local Inference category.
SUCCESS – Chompie of IBM X-Force Offensive Research (XOR) used a race condition to escalate privileges on Red Hat Enterprise Linux for Workstations, earning $20,000 and 2 Master of Pwn points.


COLLISON – Although successful on stage, @rewhiles of Viettel Cyber Security (@vcslab) targeting Anthropic Claude Code in the Coding Agent category used a bug that was previously known to the vendor. They still earn $20,000 and 2 Master of Pwn points



SUCCESS – haehae (@haehaeYang) of Out Of Bounds used a Path Traversal bug to exploit NVIDIA Megatron Bridge in the second round, earning $10,000 and 2 Master of Pwn points. Full win!


SUCCESS – Kentaro Kawane of GMO Cybersecurity by Ierae chained 2 Use-After-Free bugs to escalate privileges on Microsoft Windows 11 in the third round, earning $15,000 and 3 Master of Pwn points.








