


Year: 2025
ZDI-25-407: SolarWinds Web Help Desk AjaxProxy Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of SolarWinds Web Help Desk. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2024-28988.
ZDI-25-406: SolarWinds Serv-U FTP Service Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of SolarWinds Serv-U. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5. The following CVEs are assigned: CVE-2024-45711.
ZDI-25-405: Fuji Electric Smart Editor X1 File Parsing Stack-based Buffer Overflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Fuji Electric Smart Editor. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-41388.
ZDI-25-404: Fuji Electric Smart Editor X1 File Parsing Stack-based Buffer Overflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Fuji Electric Smart Editor. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-41388.
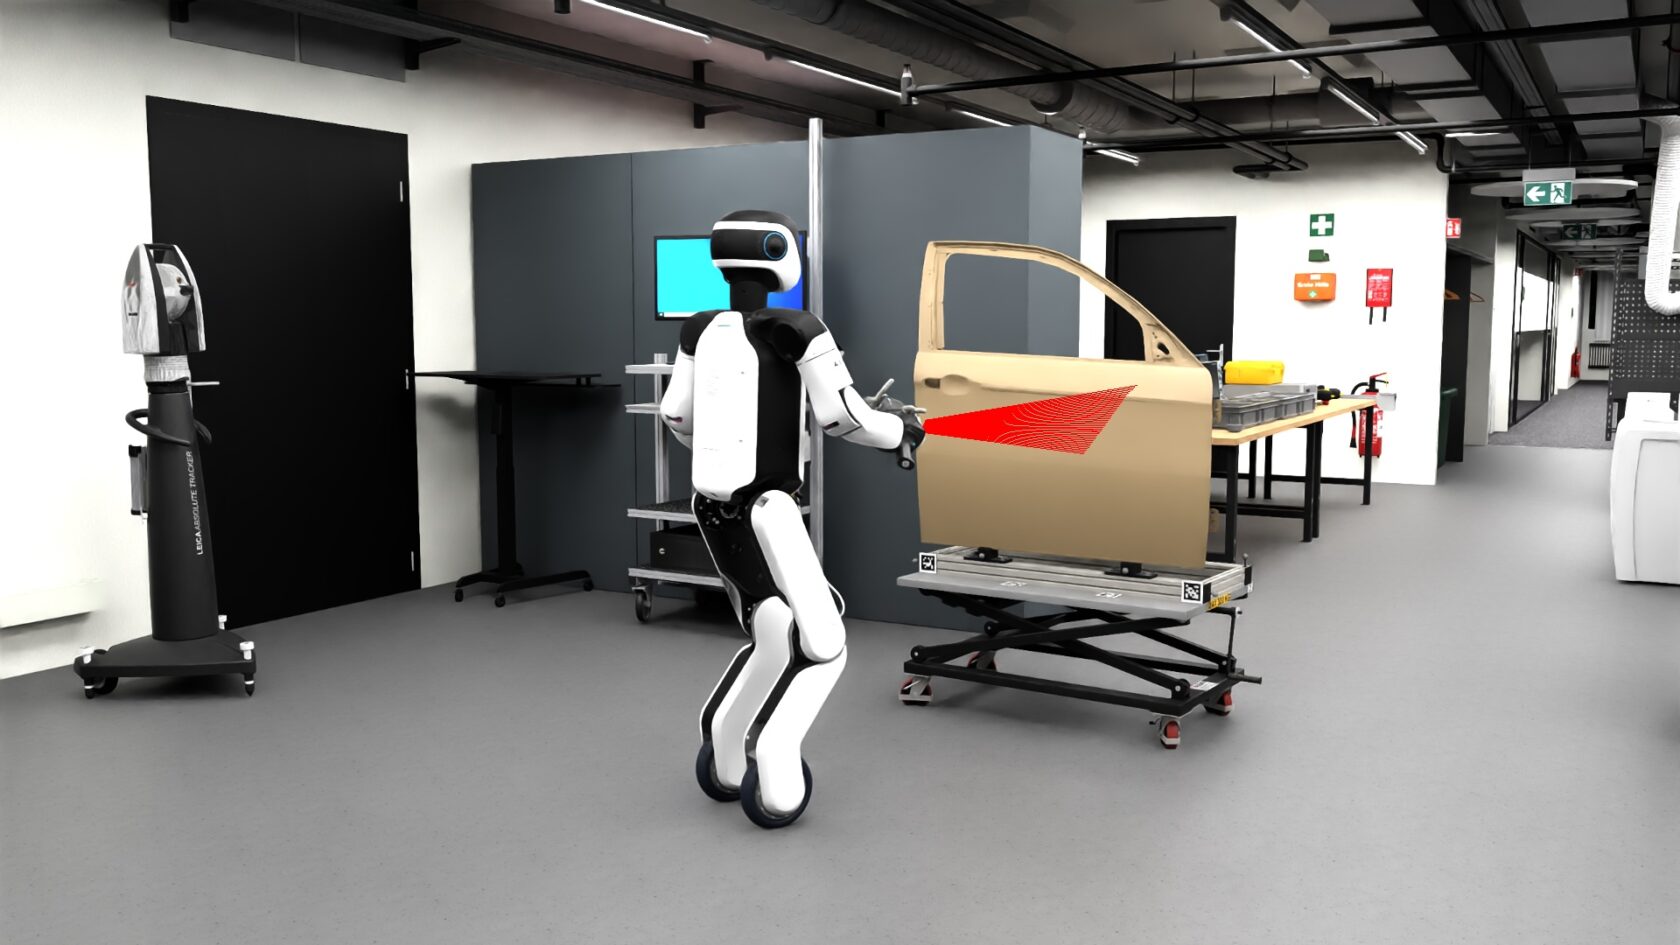
Hexagon Taps NVIDIA Robotics and AI Software to Build and Deploy AEON, a New Humanoid
As a global labor shortage leaves 50 million positions unfilled across industries like manufacturing and logistics, Hexagon — a global leader in measurement technologies — is developing humanoid robots that can lend a helping hand. Industrial sectors depend on skilled workers to perform a variety of error-prone tasks, including operating high-precision scanners for reality capture …
Hexagon Taps NVIDIA Robotics and AI Software to Build and Deploy AEON, a New HumanoidRead More
ZDI-25-396: Siemens TeleControl Server Basic UpdateOpcSettings SQL Injection Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Siemens TeleControl Server Basic. Although authentication is required to exploit this vulnerability, the existing authentication mechanism can be bypassed. The ZDI has assigned a CVSS rating of 6.5. The following CVEs are assigned: CVE-2025-31353.
ZDI-25-395: Siemens TeleControl Server Basic UpdateGateways SQL Injection Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Siemens TeleControl Server Basic. Although authentication is required to exploit this vulnerability, the existing authentication mechanism can be bypassed. The ZDI has assigned a CVSS rating of 6.5. The following CVEs are assigned: CVE-2025-31352.
ZDI-25-394: Siemens TeleControl Server Basic CreateProject SQL Injection Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Siemens TeleControl Server Basic. Although authentication is required to exploit this vulnerability, the existing authentication mechanism can be bypassed. The ZDI has assigned a CVSS rating of 6.5. The following CVEs are assigned: CVE-2025-31351.
ZDI-25-393: Siemens TeleControl Server Basic UpdateBufferingSettings SQL Injection Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Siemens TeleControl Server Basic. Although authentication is required to exploit this vulnerability, the existing authentication mechanism can be bypassed. The ZDI has assigned a CVSS rating of 6.5. The following CVEs are assigned: CVE-2025-31350.
ZDI-25-380: Trend Micro Maximum Security Platinum Host Service Link Following Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Trend Micro Maximum Security. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-49385.






