


ZDI-26-294: (0Day) Microsoft Windows library-ms NTLM Response Information Disclosure Vulnerability
This vulnerability allows network-adjacent attackers to disclose sensitive information on affected installations of Microsoft Windows. User interaction is required to exploit this vulnerability in that the target must view a folder containing malicious content. The ZDI has assigned a CVSS rating of 3.5.
ZDI-26-293: (0Day) Microsoft Office URI Handler NTLM Response Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose NTLM responses on affected installations of Microsoft Office. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 4.3.
Autonomous AI at Scale: Adobe Agents Unlock Breakthrough Creative Intelligence With NVIDIA and WPP
AI agents are transforming how work gets done across all industries, accelerating everything from content creation to decision-making. NVIDIA’s expanded strategic collaborations with Adobe and WPP are bringing agentic AI to the center of enterprise marketing operations across creative production and customer experience orchestration. As demand for personalized customer experiences surges, brands require intelligent systems …
NVIDIA and Partners Showcase the Future of AI-Driven Manufacturing at Hannover Messe 2026
Manufacturing is at an inflection point. Across every major industrial economy, the pressure to do more with less — due to faster design cycles, leaner operations and strain on skilled labor pools — is accelerating the shift to AI-driven production. The question is no longer whether to adopt AI, but how fast and at what …
NVIDIA and Partners Showcase the Future of AI-Driven Manufacturing at Hannover Messe 2026Read More
No Need for Space Gear — Capcom’s ‘PRAGMATA’ Joins GeForce NOW on Launch Day
Head straight for orbit with GeForce NOW — no space helmet required. PRAGMATA, Capcom’s long-awaited sci-fi action adventure, touches down on GeForce NOW the same day it launches worldwide. The futuristic journey through a cold lunar station in the near future can be streamed instantly from the cloud to almost any device, no console or …
No Need for Space Gear — Capcom’s ‘PRAGMATA’ Joins GeForce NOW on Launch DayRead More
ZDI-26-292: QNAP TS-453E QVRPro excpostgres Exposed Dangerous Method Remote Code Execution Vulnerability
This vulnerability allows network-adjacent attackers to execute arbitrary code on affected installations of QNAP TS-453E devices. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2026-22898.
ZDI-26-291: NI LabVIEW LVCLASS File Parsing Memory Corruption Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of NI LabVIEW. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2026-32861.
ZDI-26-290: NI LabVIEW LVLIB File Parsing Memory Corruption Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of NI LabVIEW. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2026-32860.
ZDI-26-289: Linux Kernel ETS Scheduler Race Condition Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Linux Kernel. An attacker must first obtain the ability to execute high-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5. The following CVEs are assigned: CVE-2025-71066.
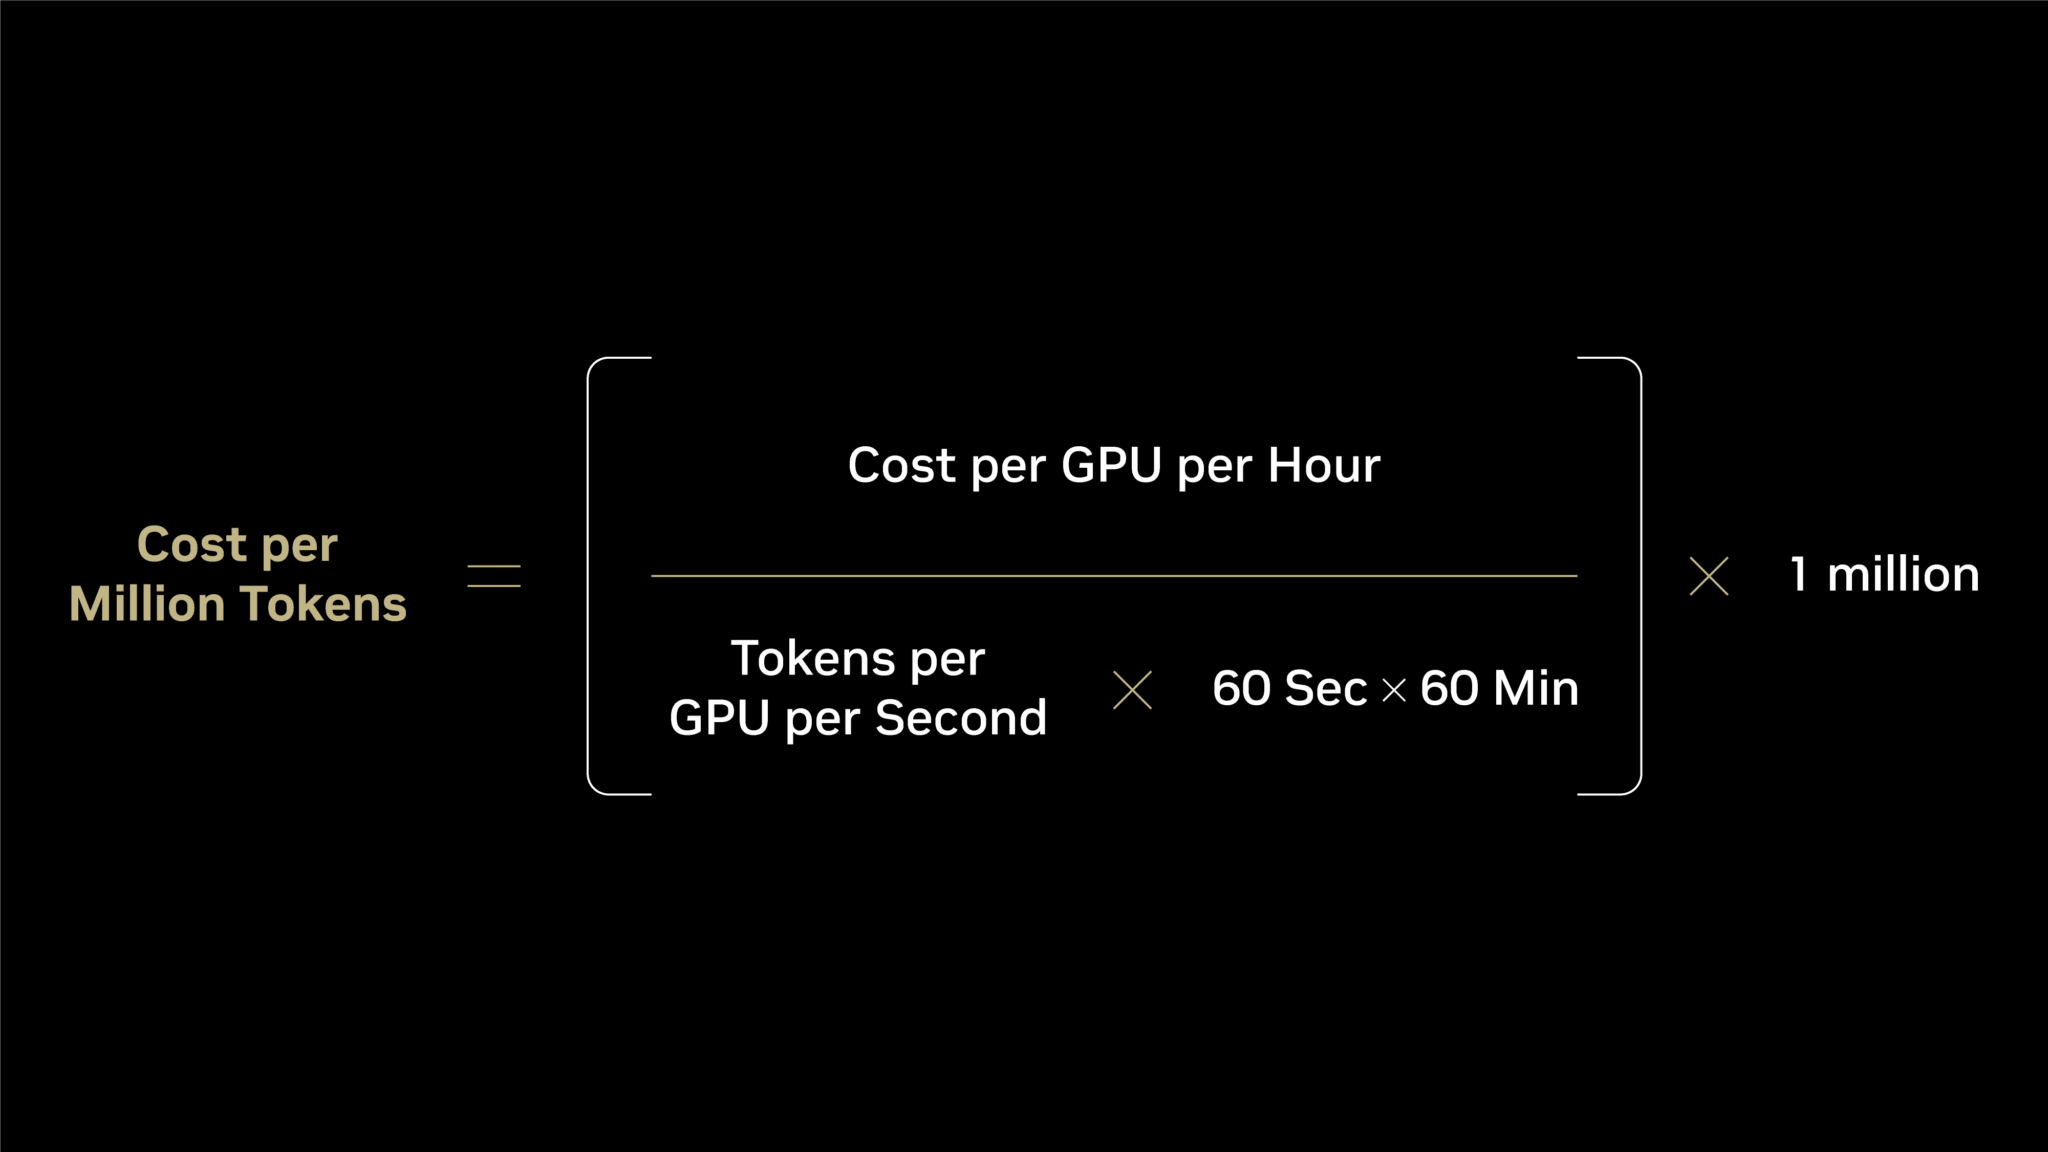
Rethinking AI TCO: Why Cost per Token Is the Only Metric That Matters
Traditional data centers only stored, retrieved and processed data. In the generative and agentic AI era, these facilities have evolved into AI token factories. With AI inference becoming their primary workload, their primary output is intelligence manufactured in the form of tokens. This transformation demands a corresponding shift in how the economics of AI infrastructure, …
Rethinking AI TCO: Why Cost per Token Is the Only Metric That MattersRead More






