


ZDI-24-1031: NI VeriStand NIVSPRJ File Parsing Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of NI VeriStand. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-6675.
Breaking Barriers and Assumptions: Techniques for Privilege Escalation on Windows: Part 1
The number of link following vulnerabilities submitted to the Trend Micro ZDI program has been increasing rapidly over the past several years. These submissions have provided us with insight into how these vulnerabilities are being found and exploited. In years prior we were seeing a lot of low-hanging fruit in this bug class where you …
Breaking Barriers and Assumptions: Techniques for Privilege Escalation on Windows: Part 1Read More
ZDI-24-1020: SolarWinds Access Rights Manager deleteTransferFile Directory Traversal Arbitrary File Deletion and Information Disclosure Vulnerability
This vulnerability allows remote attackers to delete arbitrary files and disclose sensitive information on affected installations of SolarWinds Access Rights Manager. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.6. The following CVEs are assigned: CVE-2024-28992.
ZDI-24-1019: (Pwn2Own) Docker Desktop extension-manager Exposed Dangerous Function Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Docker Desktop. An attacker must first obtain the ability to execute high-privileged code within the container in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.2. The following CVEs are assigned: CVE-2024-6222.
ZDI-24-1018: (Pwn2Own) Linux Kernel io_uring Buffer List Race Condition Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Linux Kernel. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-35880.
ZDI-24-1017: (0Day) Panda Security Dome Link Following Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Panda Security Dome. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-7242.
Creators To Have Personalized AI Assistants, Meta CEO Mark Zuckerberg Tells NVIDIA CEO Jensen Huang
In a highly anticipated fireside chat at SIGGRAPH 2024, NVIDIA founder and CEO Jensen Huang and Meta founder and CEO Mark Zuckerberg discussed the transformative potential of open source AI and AI assistants. Zuckerberg kicked off the discussion by announcing the launch of AI Studio, a new platform that allows users to create, share and …
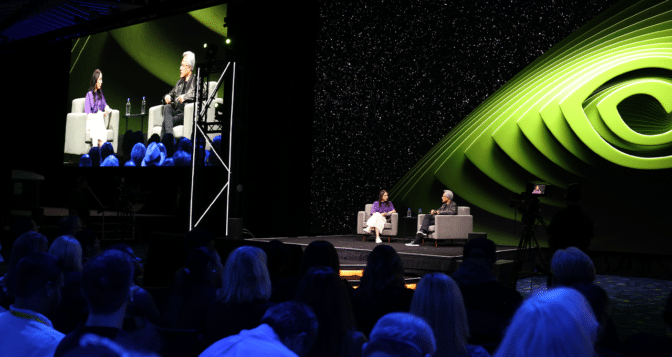
‘Everybody Will Have an AI Assistant,’ NVIDIA CEO Tells SIGGRAPH Audience
The generative AI revolution — with deep roots in visual computing — is amplifying human creativity even as accelerated computing promises significant gains in energy efficiency, NVIDIA founder and CEO Jensen Huang said Monday. That makes this week’s SIGGRAPH professional graphics conference, in Denver, the logical venue to discuss what’s next. “Everybody will have an …
‘Everybody Will Have an AI Assistant,’ NVIDIA CEO Tells SIGGRAPH AudienceRead More
ZDI-24-974: IrfanView CIN File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of IrfanView. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-6822.
ZDI-24-973: IrfanView CIN File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of IrfanView. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-6821.






