


GeForce NOW Celebrates 2,000 Games in the Cloud
Editor’s note: An earlier version of this article included ‘Warhammer 40:000 Speed Freeks.’ The game will not be available this week. This GFN Thursday marks 2,000 games in the GeForce NOW library, with four new games joining this week, alongside a demo for Square Enix’s Visions of Mana and a new reward for members playing Elder …
Recursion CEO Chris Gibson on Accelerating the Biopharmaceutical Industry With AI
Techbio is a field combining data, technology and biology to enhance scientific processes — and AI has the potential to supercharge the biopharmaceutical industry further. In this episode of NVIDIA’s AI Podcast, host Noah Kravitz speaks with Chris Gibson, cofounder and CEO of Recursion, about how the company uses AI and machine learning to accelerate …
Recursion CEO Chris Gibson on Accelerating the Biopharmaceutical Industry With AIRead More
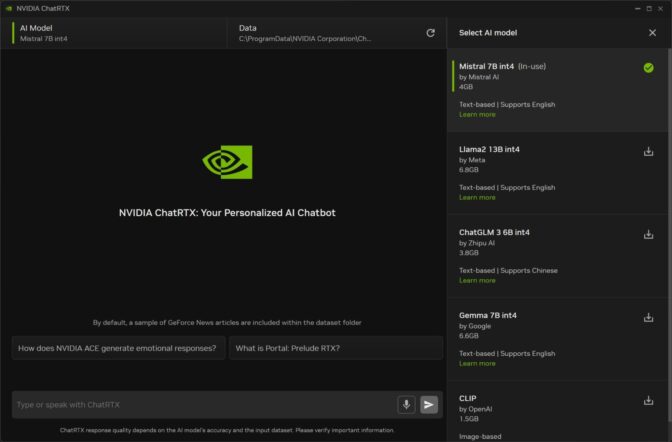
Problem Solved: STEM Studies Supercharged With RTX and AI Technologies
Editor’s note: This post is part of the AI Decoded series, which demystifies AI by making the technology more accessible, and showcases new hardware, software, tools and accelerations for RTX PC users. AI powered by NVIDIA GPUs is accelerating nearly every industry, creating high demand for graduates, especially from STEM fields, who are proficient in …
Problem Solved: STEM Studies Supercharged With RTX and AI TechnologiesRead More
ZDI-24-1101: Apple macOS Metal Framework KTX Image Parsing Out-Of-Bounds Read Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Apple macOS. Interaction with the Metal framework is required to exploit this vulnerability but attack vectors may vary depending on the implementation. The ZDI has assigned a CVSS rating of 3.3. The following CVEs are assigned: CVE-2024-27802.
ZDI-24-1100: SMARTBEAR SoapUI unpackageAll Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of SMARTBEAR SoapUI. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-7565.
ZDI-24-1099: Apache OFBiz resolveURI Authentication Bypass Vulnerability
This vulnerability allows remote attackers to bypass authentication on affected installations of Apache OFBiz. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2024-38856.
ZDI-24-1098: (0Day) Microsoft Windows Error Reporting Service Missing Authorization Arbitrary Process Termination Vulnerability
This vulnerability allows local attackers to create a denial-of-service condition on affected installations of Microsoft Windows. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 5.5.
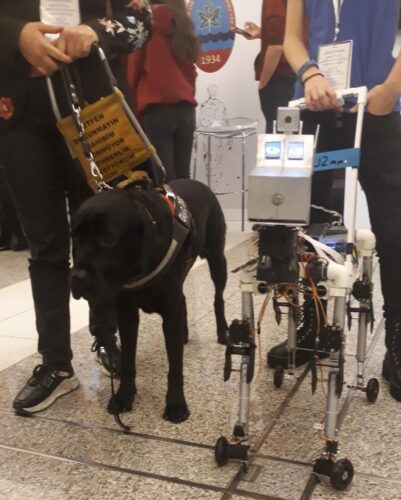
Meet the Maker: High School Student Develops Robot Guide Dogs With NVIDIA Jetson
High school student Selin Alara Ornek is looking ahead — using machine learning and the NVIDIA Jetson platform for edge AI and robotics to create robot guide dogs for the visually impaired. The project, called IC4U, is one of seven robots Ornek has created to date, including a school aid robot, named BB4All, that can …
Meet the Maker: High School Student Develops Robot Guide Dogs With NVIDIA JetsonRead More
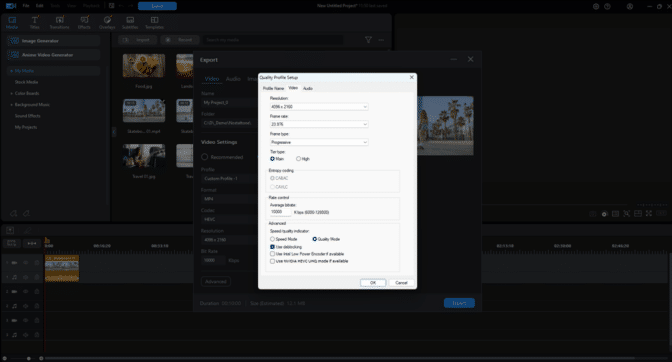
Editor’s Paradise: NVIDIA RTX-Powered Video Software CyberLink PowerDirector Gains High-Efficiency Video Coding Upgrades
Editor’s note: This post is part of our In the NVIDIA Studio series, which celebrates featured artists, offers creative tips and tricks, and demonstrates how NVIDIA Studio technology improves creative workflows. We’re also deep diving on new GeForce RTX GPU features, technologies and resources, and how they dramatically accelerate content creation. Every month brings new …
ZDI-24-1087: (0Day) oFono SMS Decoder Stack-based Buffer Overflow Privilege Escalation Vulnerability
This vulnerability allows local attackers to execute arbitrary code on affected installations of oFono. An attacker must first obtain the ability to execute code on the target modem in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.0. The following CVEs are assigned: CVE-2024-7547.






