


Category: News
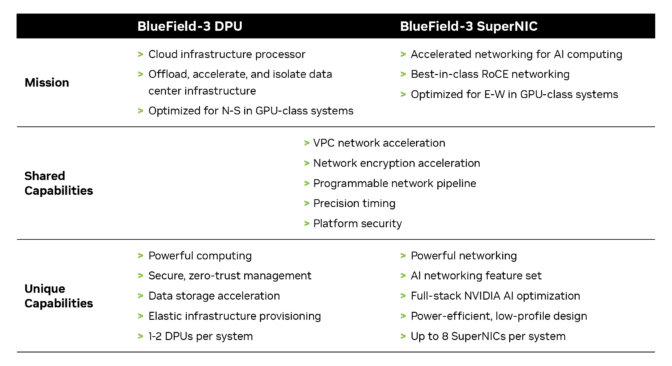
What Is a SuperNIC?
Generative AI is the latest turn in the fast-changing digital landscape. One of the groundbreaking innovations making it possible is a relatively new term: SuperNIC. What Is a SuperNIC? SuperNIC is a new class of network accelerators designed to supercharge hyperscale AI workloads in Ethernet-based clouds. It provides lightning-fast network connectivity for GPU-to-GPU communication, achieving …
AI to See ‘Major Second Wave,’ NVIDIA CEO Says in Fireside Chat With iliad Group Exec
European startups will get a massive boost from a new generation of AI infrastructure, NVIDIA founder and CEO Jensen Huang said Friday in a fireside chat with iliad Group Deputy CEO Aude Durand — and it’s coming just in time. “We’re now seeing a major second wave,” Huang said of the state of AI during …
AI to See ‘Major Second Wave,’ NVIDIA CEO Says in Fireside Chat With iliad Group ExecRead More
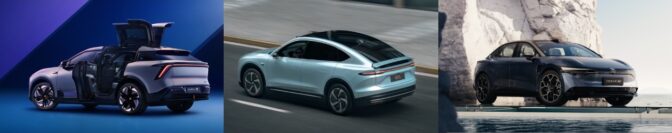
From Guangzhou to Los Angeles, Automakers Dazzle With AI-Powered Vehicles
Good news for car lovers: Two acclaimed auto shows, taking place now through next week, are delighting attendees with displays of next-generation automotive designs powered by AI. Hundreds of thousands of auto enthusiasts worldwide are expected to visit Guangzhou, China — known as the city of flowers — to attend its auto show, running through …
From Guangzhou to Los Angeles, Automakers Dazzle With AI-Powered VehiclesRead More
ZDI-23-1716: Luxion KeyShot Viewer KSP File Parsing Memory Corruption Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Luxion KeyShot Viewer. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2023-22139.
Three Ways Generative AI Can Bolster Cybersecurity
Human analysts can no longer effectively defend against the increasing speed and complexity of cybersecurity attacks. The amount of data is simply too large to screen manually. Generative AI, the most transformative tool of our time, enables a kind of digital jiu jitsu. It lets companies shift the force of data that threatens to overwhelm …
AI Training AI: GatorTronGPT at the Forefront of University of Florida’s Medical AI Innovations
How do you train an AI to understand clinical language with less clinical data? Train another AI to synthesize training data. Artificial intelligence is changing the way medicine is done, and is increasingly being used in all sorts of clinical tasks. This is fueled by generative AI and models like GatorTronGPT, a generative language model …
ZDI-23-1715: ManageEngine Applications Manager SingleSignOn Cross-Site Scripting Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of ManageEngine Applications Manager. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2023-38333.
ZDI-23-1714: Adobe Animate FLA File Parsing Out-Of-Bounds Read Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Adobe Animate. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 3.3. The following CVEs are assigned: CVE-2023-44325.
ZDI-23-1713: Adobe Acrobat Reader DC Font Parsing Out-Of-Bounds Read Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Adobe Acrobat Reader DC. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2023-44337.
ZDI-23-1712: Adobe Acrobat Reader DC Annotation Out-Of-Bounds Read Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Adobe Acrobat Reader DC. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2023-44338.






