


Category: News
ZDI-24-1037: PDF-XChange Editor PDF File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of PDF-XChange Editor. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-7352.
ZDI-24-1038: PaperCut NG pc-web-print Link Following Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of PaperCut NG Server. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-3037.
ZDI-24-1039: PaperCut NG web-print-hot-folder Link Following Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of PaperCut NG. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-3037.
ZDI-24-1040: Apple macOS AppleVADriver Out-Of-Bounds Read Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Apple macOS. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 4.3. The following CVEs are assigned: CVE-2024-27877.
Breaking Barriers and Assumptions: Techniques for Privilege Escalation on Windows: Part 2
The number of vulnerabilities that we see through the program provides significant insight into the attack surfaces of each product that we purchase bugs in. These submissions sometimes reveal not only potential variants but also broader architectural flaws. Submitters frequently choose to provide a full exploit with their submission, which can further reveal interesting techniques. …
Breaking Barriers and Assumptions: Techniques for Privilege Escalation on Windows: Part 2Read More
NVIDIA Researchers Harness Real-Time Gen AI to Build Immersive Desert World
NVIDIA researchers used NVIDIA Edify, a multimodal architecture for visual generative AI, to build a detailed 3D desert landscape within a few minutes in a live demo at SIGGRAPH’s Real-Time Live event on Tuesday. During the event — one of the prestigious graphics conference’s top sessions — NVIDIA researchers showed how, with the support of …
NVIDIA Researchers Harness Real-Time Gen AI to Build Immersive Desert WorldRead More
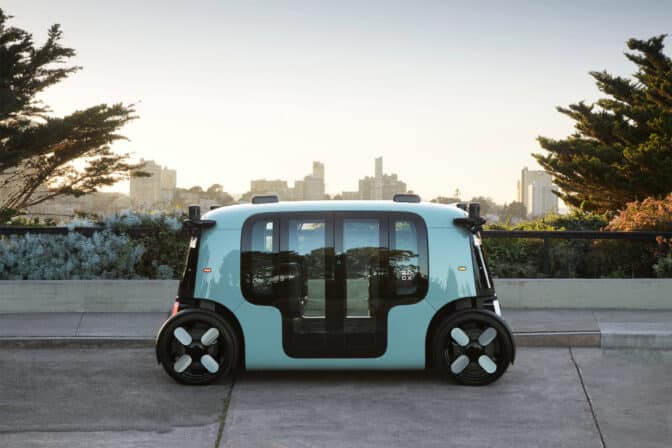
NVIDIA and Zoox Pave the Way for Autonomous Ride-Hailing
In celebration of Zoox’s 10th anniversary, NVIDIA founder and CEO Jensen Huang recently joined the robotaxi company’s CEO, Aicha Evans, and its cofounder and CTO, Jesse Levinson, to discuss the latest in autonomous vehicle (AV) innovation and experience a ride in the Zoox robotaxi. In a fireside chat at Zoox’s headquarters in Foster City, Calif., …
NVIDIA and Zoox Pave the Way for Autonomous Ride-HailingRead More
ZDI-24-1031: NI VeriStand NIVSPRJ File Parsing Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of NI VeriStand. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-6675.
ZDI-24-1032: NI FlexLogger Redis Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of NI FlexLogger. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-6121.
ZDI-24-1033: NI FlexLogger Redis Server Incorrect Permission Assignment Information Disclosure Vulnerability
This vulnerability allows local attackers to disclose sensitive information on affected installations of NI FlexLogger. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 5.5. The following CVEs are assigned: CVE-2024-6122.






