


Author: admin
ZDI-25-1036: Tencent TFace restore_checkpoint Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Tencent TFace. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-13709.
ZDI-25-1035: Tencent TFace eval Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Tencent TFace. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-13711.

At NeurIPS, NVIDIA Advances Open Model Development for Digital and Physical AI
Researchers worldwide rely on open-source technologies as the foundation of their work. To equip the community with the latest advancements in digital and physical AI, NVIDIA is further expanding its collection of open AI models, datasets and tools — with potential applications in virtually every research field. At NeurIPS, one of the world’s top AI …
At NeurIPS, NVIDIA Advances Open Model Development for Digital and Physical AIRead More
ZDI-25-1026: Appleton UPSMON-PRO UPSMONProService Stack-based Buffer Overflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Appleton UPSMON-PRO. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2024-3871.
ZDI-25-1025: MariaDB mariadb-dump Utility Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of MariaDB. Interaction with the mariadb-dump utility is required to exploit this vulnerability but attack vectors may vary depending on the implementation. The ZDI has assigned a CVSS rating of 7.0. The following CVEs are assigned: CVE-2025-13699.
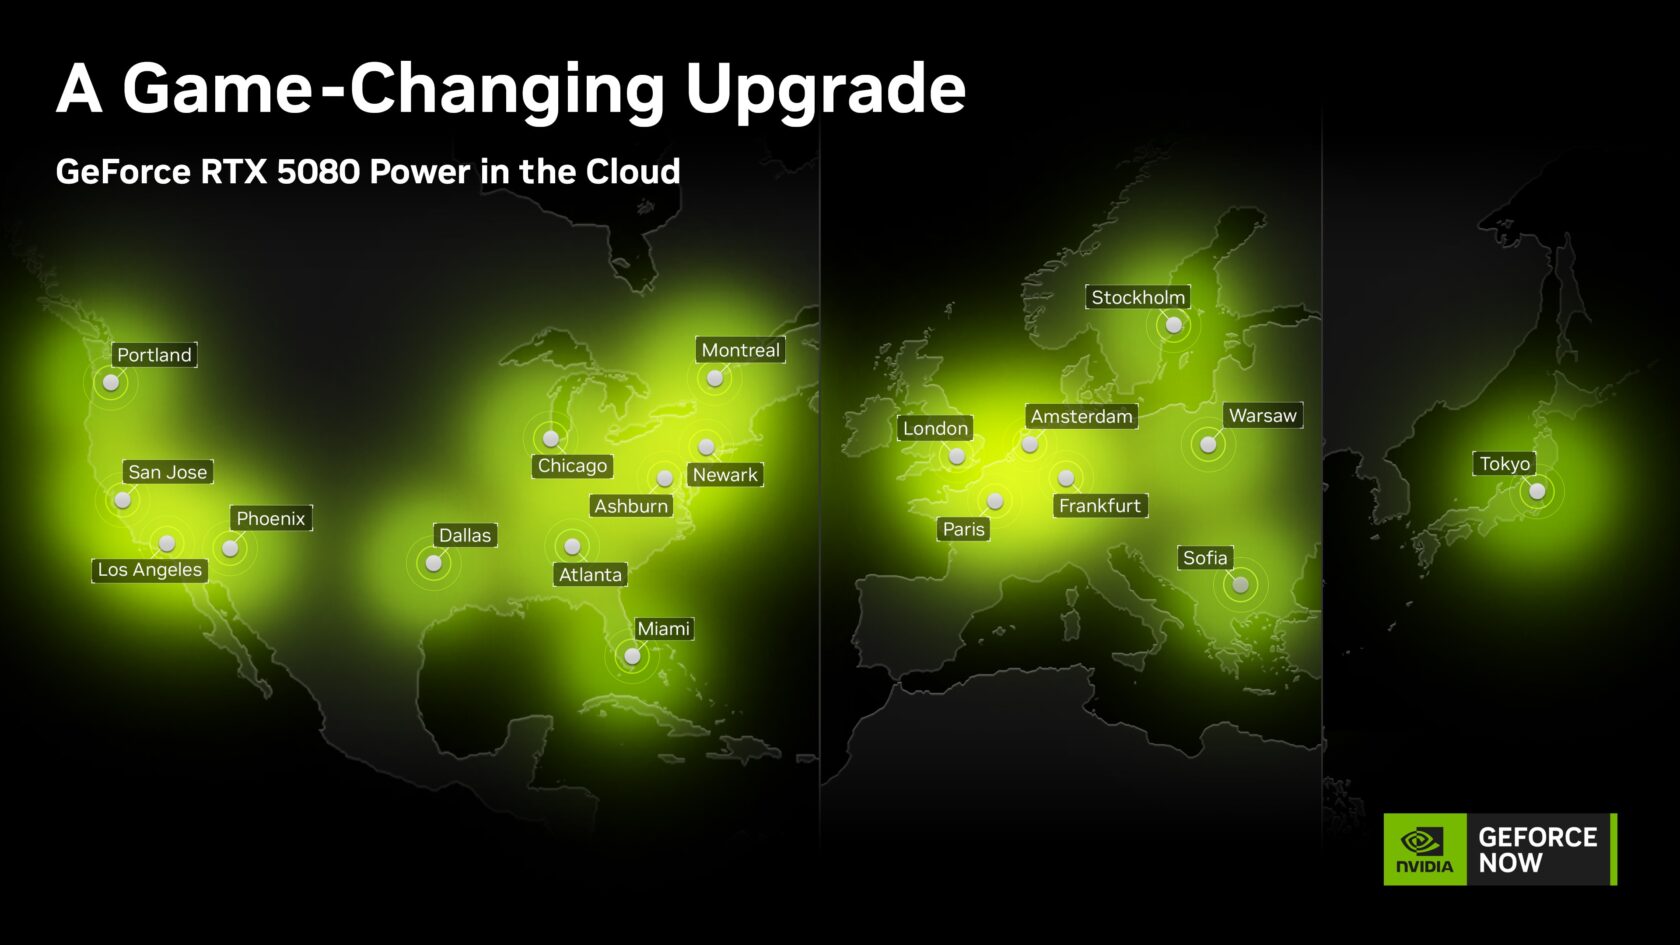
The Ultimate Black Friday Deal Is Here
Black Friday is leveling up. Get ready to score one of the biggest deals of the season — 50% off the first three months of a new GeForce NOW Ultimate membership. That’s GeForce RTX 5080-class power in the cloud for half the price. The completed Ultimate upgrade. The NVIDIA Blackwell RTX upgrade is now fully …
ZDI-25-1024: DreamFactory saveZipFile Command Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of DreamFactory. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2025-13700.
ZDI-25-1023: VIPRE Advanced Security Incorrect Permission Assignment Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of VIPRE Advanced Security for PC. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-13703.
ZDI-25-1022: Deciso OPNsense diag_backup.php filename Directory Traversal Arbitrary File Creation Vulnerability
This vulnerability allows network-adjacent attackers to create arbitrary files on affected installations of Deciso OPNsense. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 4.5. The following CVEs are assigned: CVE-2025-13698.






