


Author: admin
Looking at the Attack Surfaces of the Kenwood DMX958XR IVI
In our previous Kenwood DMX958XR blog post, we detailed the internals of the Kenwood in-vehicle infotainment (IVI) head unit and provided annotated pictures of each PCB. In this post, we aim to outline the attack surface of the DMX958XR in the hopes of providing inspiration for vulnerability research. We will cover the main supported technologies …
Looking at the Attack Surfaces of the Kenwood DMX958XR IVIRead More
Efficiency Meets Personalization: How AI Agents Improve Customer Service
Editor’s note: This post is the first in the AI On blog series, which explores the latest techniques and real-world applications of agentic AI, chatbots and copilots. The series will also highlight the NVIDIA software and hardware powering advanced AI agents, which form the foundation of AI query engines that gather insights and perform tasks …
Efficiency Meets Personalization: How AI Agents Improve Customer ServiceRead More
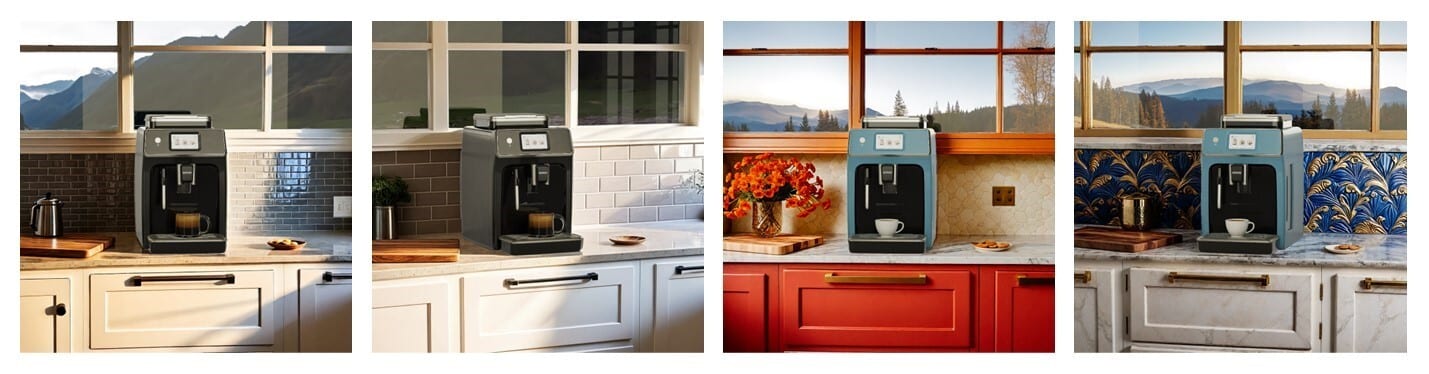
Into the Omniverse: How Generative AI Fuels Personalized, Brand-Accurate Visuals With OpenUSD
Editor’s note: This post is part of Into the Omniverse, a blog series focused on how developers, 3D artists and enterprises can transform their workflows using the latest advances in OpenUSD and NVIDIA Omniverse. 3D product configurators are changing the way industries like retail and automotive engage with customers by offering interactive, customizable 3D visualizations …
ZDI-24-1534: Microsoft SharePoint Server FindSpecific Unsafe Reflection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Microsoft SharePoint Server. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2024-38024.
ZDI-24-1533: Panda Security Dome PSANHost Link Following Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Panda Security Dome. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-8424.
ZDI-24-1532: 7-Zip Zstandard Decompression Integer Underflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of 7-Zip. Interaction with this library is required to exploit this vulnerability but attack vectors may vary depending on the implementation. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-11477.
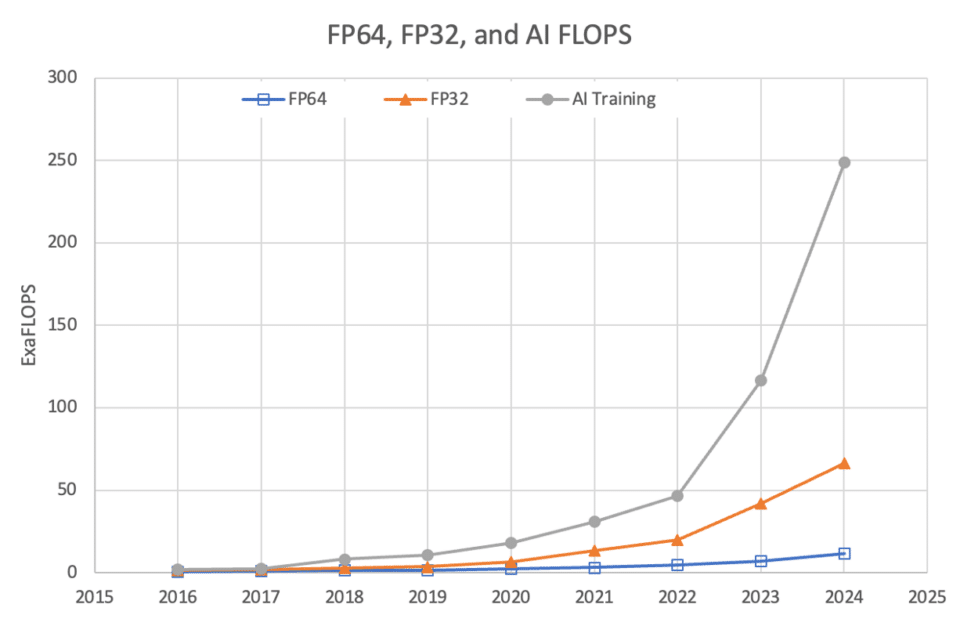
The Need for Speed: NVIDIA Accelerates Majority of World’s Supercomputers to Drive Advancements in Science and Technology
Starting with the release of CUDA in 2006, NVIDIA has driven advancements in AI and accelerated computing — and the most recent TOP500 list of the world’s most powerful supercomputers highlights the culmination of the company’s achievements in the field. This year, 384 systems on the TOP500 list are powered by NVIDIA technologies. Among the …
ZDI-24-1531: RSA Security SecureID Software Token for Microsoft Windows Uncontrolled Search Path Element Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of RSA Security SecureID Software Token for Microsoft Windows. User interaction is required to exploit this vulnerability in that the target must open a malicious file. The ZDI has assigned a CVSS rating of 7.8.
ZDI-24-1530: WordPress Core maybe_unserialize Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of WordPress Core. Authentication may be required to exploit this vulnerability, depending on the product configuration. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-31210.
ZDI-24-1529: Dassault Systèmes eDrawings Viewer X_B File Parsing Heap-based Buffer Overflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Dassault Syst��mes eDrawings Viewer. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-10204.






