


Author: admin
Detailing the Attack Surfaces of the Tesla Wall Connector EV Charger
The Tesla Wall Connector is a Level 2 electric vehicle charge station designed for use by residential home users. The device has a minimal user interface in its hardware, providing a Wi-Fi based interface for configuration and an NFC reader for user authentication. The device does not come with a dedicated mobile application out of …
Detailing the Attack Surfaces of the Tesla Wall Connector EV ChargerRead More
AI in Your Own Words: NVIDIA Debuts NeMo Retriever Microservices for Multilingual Generative AI Fueled by Data
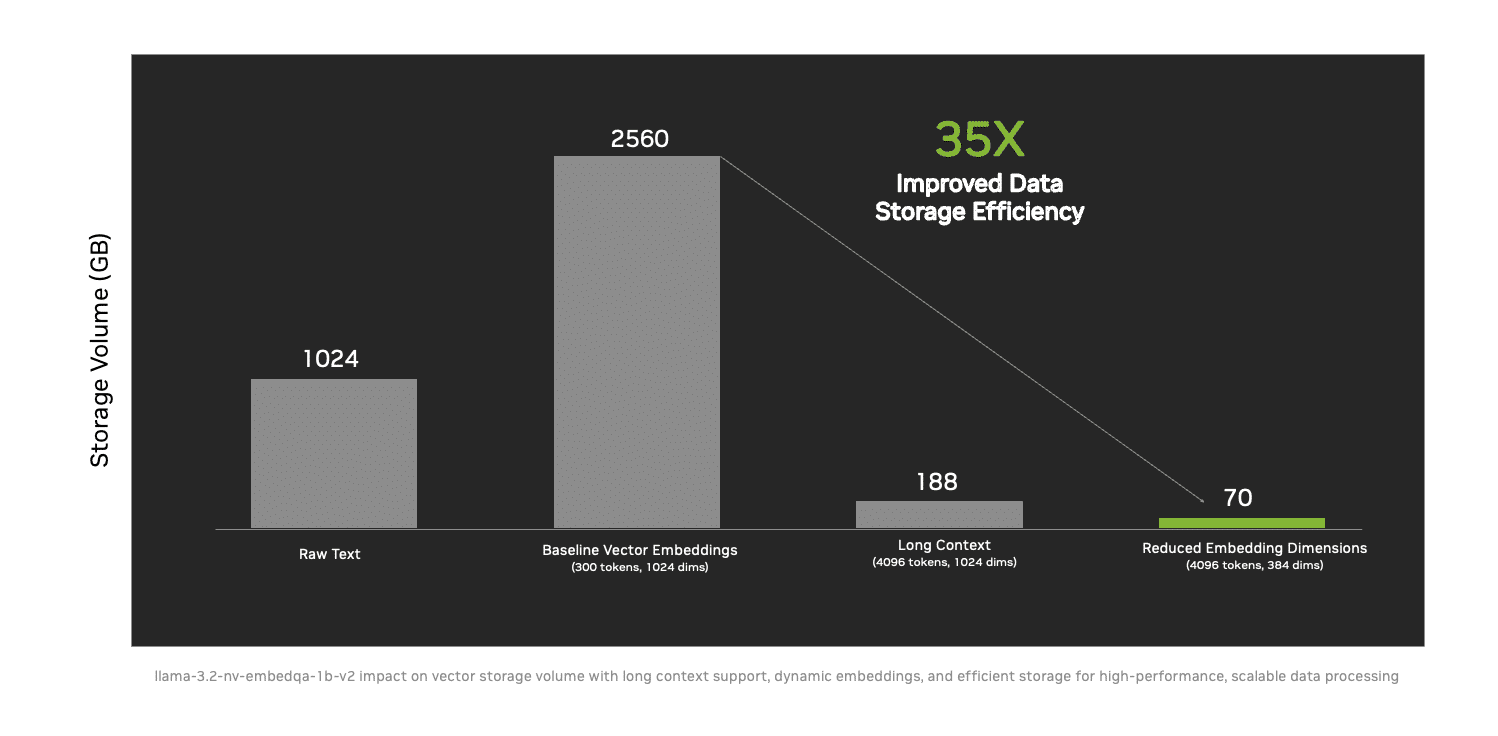
In enterprise AI, understanding and working across multiple languages is no longer optional — it’s essential for meeting the needs of employees, customers and users worldwide. Multilingual information retrieval — the ability to search, process and retrieve knowledge across languages — plays a key role in enabling AI to deliver more accurate and globally relevant …
NVIDIA Unveils Its Most Affordable Generative AI Supercomputer
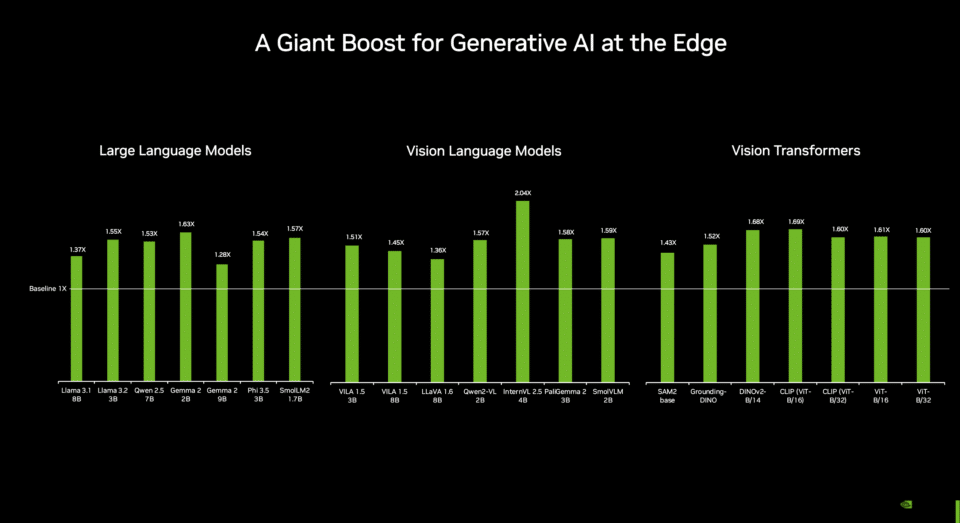
NVIDIA is taking the wraps off a new compact generative AI supercomputer, offering increased performance at a lower price with a software upgrade. The new NVIDIA Jetson Orin Nano Super Developer Kit, which fits in the palm of a hand, provides everyone from commercial AI developers to hobbyists and students, gains in generative AI capabilities …
NVIDIA Unveils Its Most Affordable Generative AI SupercomputerRead More
ZDI-24-1693: Dell Avamar Web Restore Login Action SQL Injection Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Dell Avamar. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.2. The following CVEs are assigned: CVE-2024-47484.
ZDI-24-1692: Dell Avamar Fitness Analyzer API SQL Injection Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Dell Avamar. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.1. The following CVEs are assigned: CVE-2024-47977.
ZDI-24-1691: Dell Avamar Fitness Analyzer API SQL Injection Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Dell Avamar. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.1. The following CVEs are assigned: CVE-2024-52538.
ZDI-24-1690: Dell Avamar Fitness Analyzer API SQL Injection Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Dell Avamar. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.1. The following CVEs are assigned: CVE-2024-47977.
Tech Leader, AI Visionary, Endlessly Curious Jensen Huang to Keynote CES 2025
On Jan. 6 at 6:30 p.m. PT, NVIDIA founder and CEO Jensen Huang — with his trademark leather jacket and an unwavering vision — will step onto the CES 2025 stage. From humble beginnings as a busboy at a Denny’s to founding NVIDIA, Huang’s story embodies innovation and perseverance. Huang has been named the world’s …
Tech Leader, AI Visionary, Endlessly Curious Jensen Huang to Keynote CES 2025Read More
What Is Extended Reality?
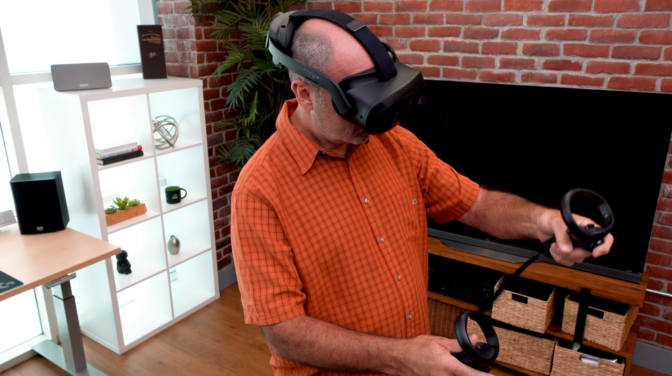
Editor’s note: This article, originally published on May 20, 2022, has been updated. Advances in extended reality have already changed the way we work, live and play, and it’s just getting started. Extended reality, or XR, is an umbrella category that covers a spectrum of newer, immersive technologies, including virtual reality, augmented reality and mixed …
ZDI-24-1688: Linux Kernel ksmbd PreviousSessionId Race Condition Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Linux Kernel. Authentication is required to exploit this vulnerability. However, only systems with ksmbd enabled are vulnerable. The ZDI has assigned a CVSS rating of 8.5.






