


Author: admin
Looking at the Attack Surfaces of the Pioneer DMH-WT7600NEX IVI
For the upcoming Pwn2Own Automotive contest, a total of four in-vehicle infotainment (IVI) head units have been selected as targets. One of these is the single-DIN Pioneer DMH-WT7600NEX. This unit offers a variety of functionality, such as wired and wireless Android Auto and Apple CarPlay, USB media playback, and more. This blog post aims to …
Looking at the Attack Surfaces of the Pioneer DMH-WT7600NEX IVIRead More
ZDI-25-032: Ivanti Endpoint Manager HIIDriver Improper Verification of Cryptographic Signature Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ivanti Endpoint Manager. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. Alternatively, no user interaction is required if the attacker has administrative credentials to the application. The ZDI …
ZDI-25-031: Ivanti Endpoint Manager MyResolveEventHandler Untrusted Search Path Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ivanti Endpoint Manager. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2024-13158.
Reviewing the Attack Surface of the Autel MaxiCharger: Part Two
Previously, we covered the internals of the Autel MaxiCharger where we highlighted each of the main components. In this post, we aim to outline the attack surface of the MaxiCharger in the hopes of providing inspiration for vulnerability research. All information has been obtained through reverse engineering, experimenting, and combing through the Autel MaxiCharger manual …
Reviewing the Attack Surface of the Autel MaxiCharger: Part TwoRead More
NVIDIA Releases NIM Microservices to Safeguard Applications for Agentic AI
AI agents are poised to transform productivity for the world’s billion knowledge workers with “knowledge robots” that can accomplish a variety of tasks. To develop AI agents, enterprises need to address critical concerns like trust, safety, security and compliance. New NVIDIA NIM microservices for AI guardrails — part of the NVIDIA NeMo Guardrails collection of …
NVIDIA Releases NIM Microservices to Safeguard Applications for Agentic AIRead More
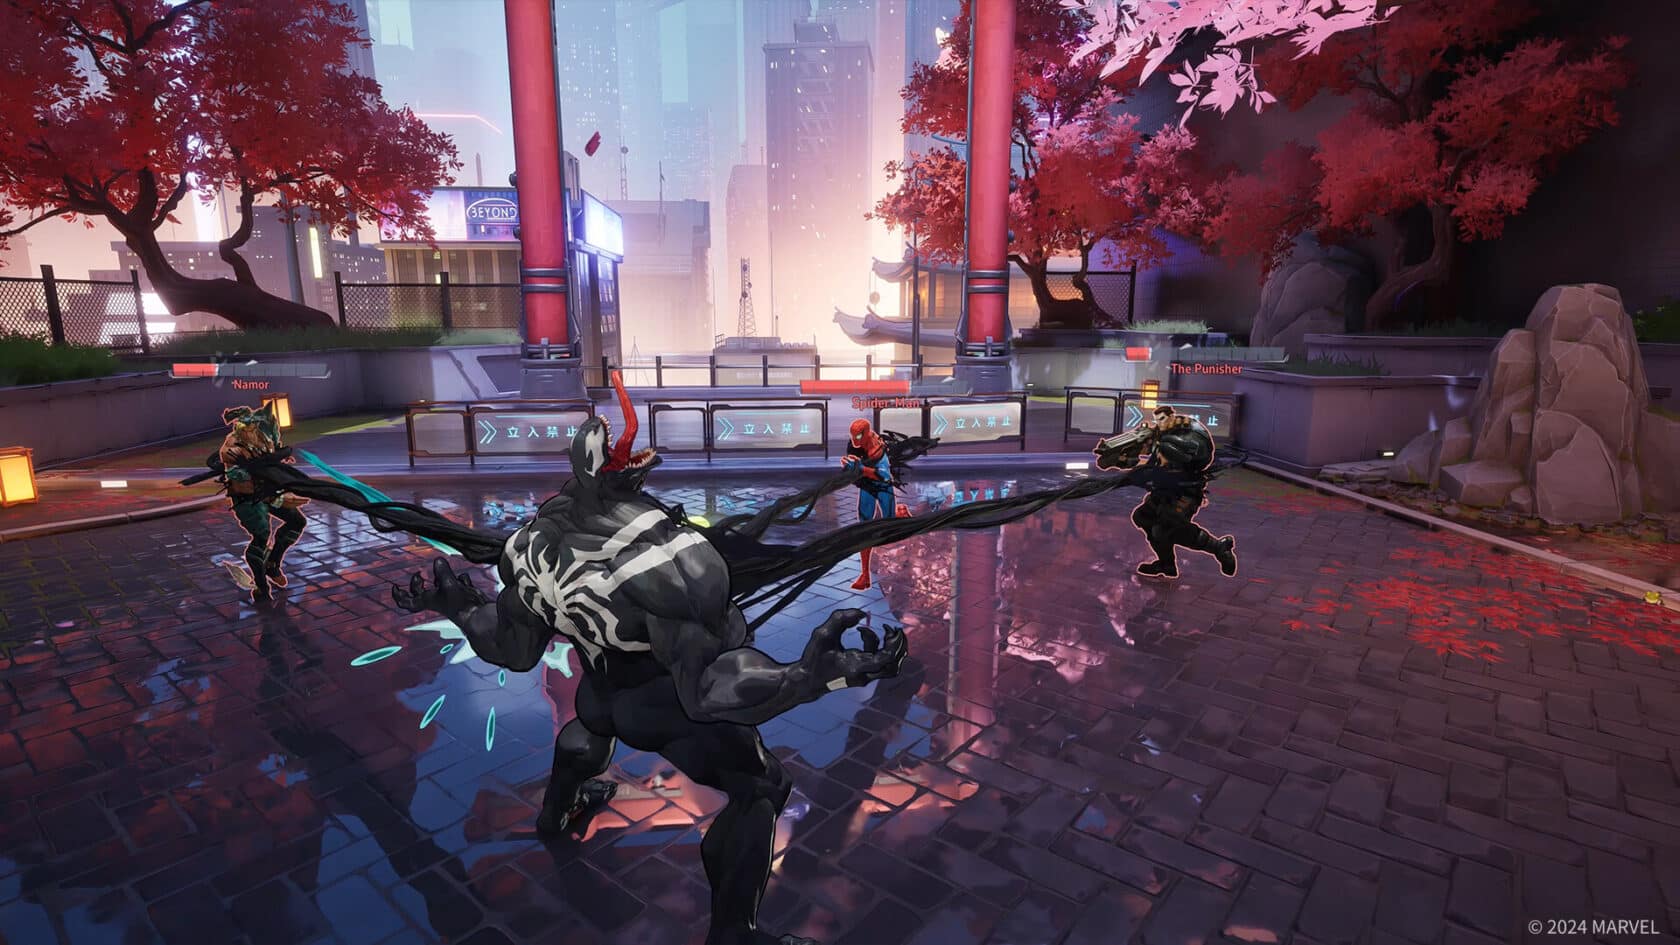
Fantastic Four-ce Awakens: Season One of ‘Marvel Rivals’ Joins GeForce NOW
Time to suit up, members. The multiverse is about to get a whole lot cloudier as GeForce NOW opens a portal to the first season of hit game Marvel Rivals from NetEase Games. Members can now game in a new dimension with expanded support for virtual- and mixed-reality devices. This week’s GeForce NOW app update …
Fantastic Four-ce Awakens: Season One of ‘Marvel Rivals’ Joins GeForce NOWRead More
ZDI-25-030: Microsoft Office Word DOCX File Parsing Uninitialized Pointer Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Microsoft Office Word. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-21363.
ZDI-25-029: Microsoft Windows Installer Service Link Following Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Microsoft Windows. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-21331.
ZDI-25-028: Microsoft Office Word RTF File Parsing Memory Corruption Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Microsoft Office Word. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-21298.
Reviewing the Attack Surface of the Autel MaxiCharger: Part One
For the upcoming Pwn2Own Automotive contest a total of 7 electric vehicle chargers have been selected. One of these is the Autel MaxiCharger AC Wallbox Commercial (MAXI US AC W12-L-4G) which also made an appearance at the inaugural Pwn2Own Automotive last January. We have previously posted internal photos of the MaxiCharger in 2023 so the …
Reviewing the Attack Surface of the Autel MaxiCharger: Part OneRead More






