


Year: 2025
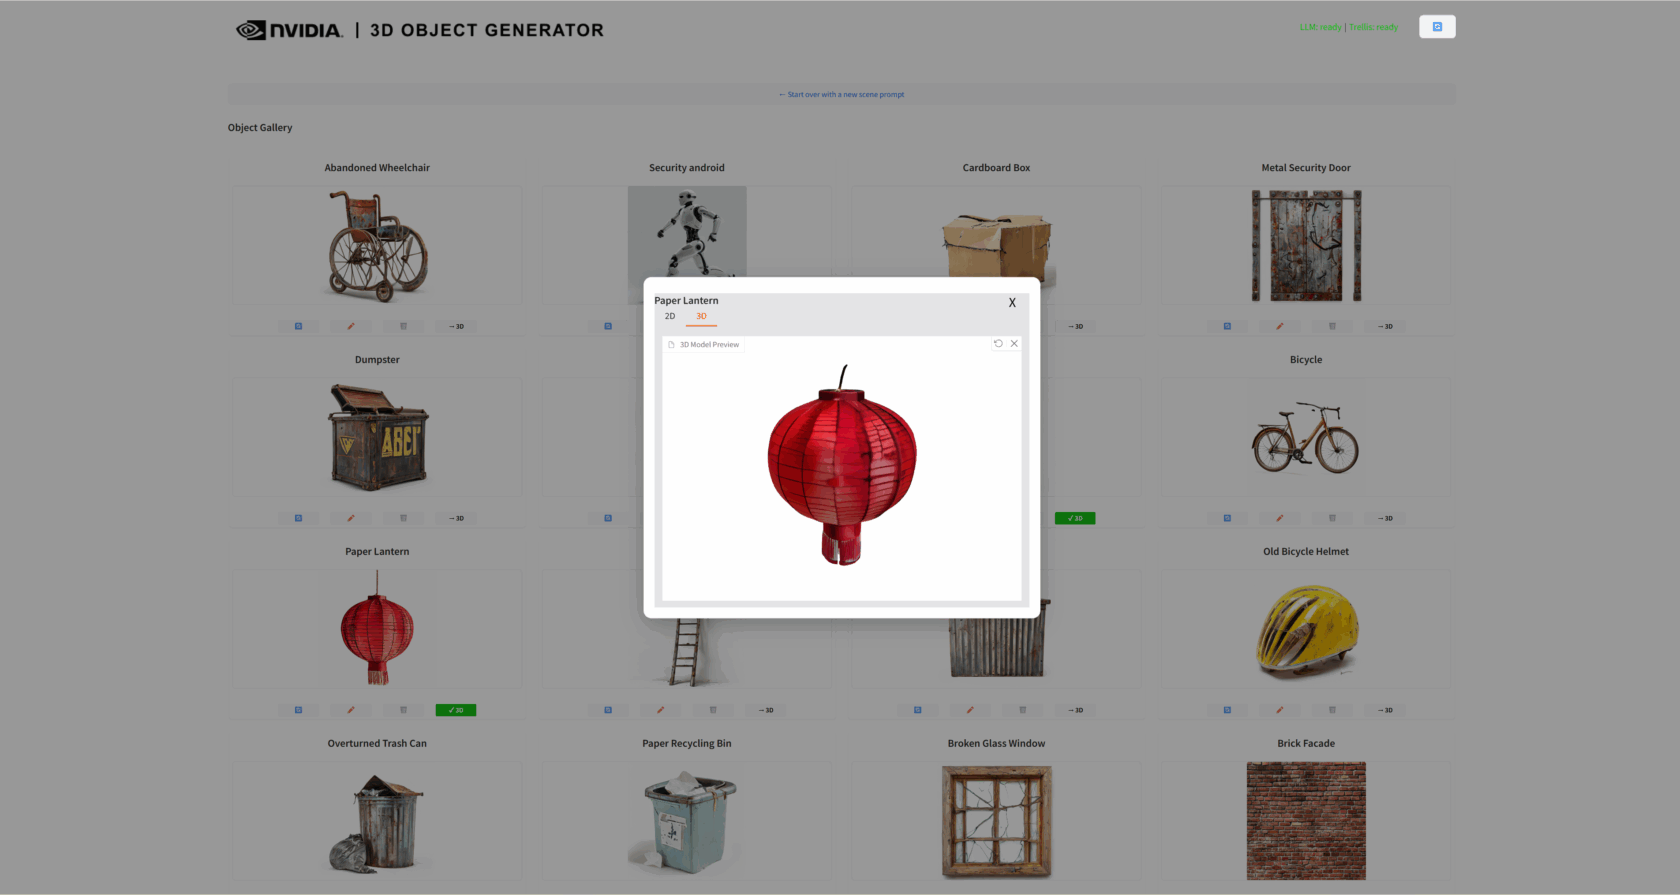
Scene It to Believe It: Populate 3D Worlds Quickly With NVIDIA AI Blueprints
3D artists are constantly prototyping. In traditional workflows, modelers must build placeholder, low-fidelity assets to populate 3D scenes, tinkering and adjusting the core elements until they’re in place. From there, visuals can be refined, detailed and finalized. Prototyping is time consuming and often comprises throwaway work, forcing artists to spend time on tedious modeling rather …
Scene It to Believe It: Populate 3D Worlds Quickly With NVIDIA AI BlueprintsRead More
ZDI-25-883: Realtek rtl81xx SDK Wi-Fi Driver rtwlanu Heap-based Buffer Overflow Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Realtek rtl81xx SDK Wi-Fi driver. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2025-8300.
ZDI-25-882: Realtek rtl81xx SDK Wi-Fi Driver MgntActSet_TEREDO_SET_RS_PACKET Heap-based Buffer Overflow Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Realtek rtl81xx SDK Wi-Fi driver. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2025-8299.
ZDI-25-881: Realtek RTL8811AU rtwlanu.sys N6CQueryInformationHandleCustomized11nOids Out-Of-Bounds Read Information Disclosure Vulnerability
This vulnerability allows local attackers to disclose sensitive information on affected installations of Realtek RTL8811AU drivers. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 3.8. The following CVEs are assigned: CVE-2025-8298.
ZDI-25-880: Realtek RTL8811AU rtwlanu.sys N6CSet_DOT11_CIPHER_DEFAULT_KEY Heap-based Buffer Overflow Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Realtek RTL8811AU drivers. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-8301.
It’s the Humidity: How International Researchers in Poland, Deep Learning and NVIDIA GPUs Could Change the Forecast
For more than a century, meteorologists have chased storms with chalkboards, equations, and now, supercomputers. But for all the progress, they still stumble over one deceptively simple ingredient: water vapor. Humidity is the invisible fuel for thunderstorms, flash floods, and hurricanes. It’s the difference between a passing sprinkle and a summer downpour that sends you …
ZDI-25-878: Apple macOS AppleIntelKBLGraphics Out-Of-Bounds Read Information Disclosure Vulnerability
This vulnerability allows local attackers to disclose sensitive information on affected installations of Apple macOS. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 6.5. The following CVEs are assigned: CVE-2025-43284.
ZDI-25-877: Delta Electronics ISPSoft ISP File Parsing Improper Control of Dynamically-Managed Code Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Delta Electronics ISPSoft. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-53419.
ZDI-25-876: Siemens Simcenter Femap NEU File Parsing Type Confusion Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Siemens Simcenter Femap. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-25175.
ZDI-25-875: Siemens Simcenter Femap NEU File Parsing Type Confusion Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Siemens Simcenter Femap. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-25175.






