


Month: October 2025
Crafting a Full Exploit RCE from a Crash in Autodesk Revit RFA File Parsing
In April of 2025, my colleague Mat Powell was hunting for vulnerabilities in Autodesk Revit 2025. While fuzzing RFA files, he found the following crash (CVE-2025-5037 / ZDI-CAN-26922, addressed by Autodesk in July 2025): Is this an exploitable crash? From the debugger output crash point as seen above, unclear whether anything is controllable. At around …
Crafting a Full Exploit RCE from a Crash in Autodesk Revit RFA File ParsingRead More
How AI-Powered Wireless Networks Will Revitalize US Global Leadership in Communications
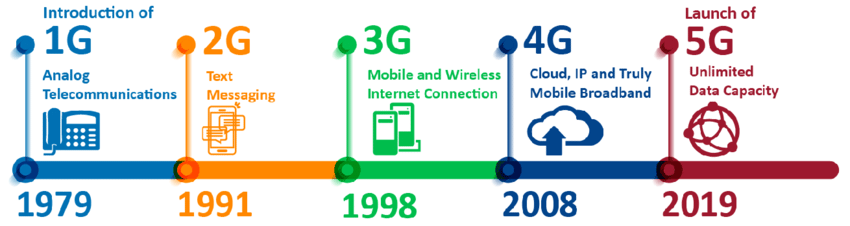
Telecommunication networks are critical infrastructure for every nation, underpinning the global flow of communications and data across billions of smartphones and connected devices. The next generation of these networks, known as 6G, will for the first time be built to support AI traffic — and can be powered by AI from the ground up. The …
How AI-Powered Wireless Networks Will Revitalize US Global Leadership in CommunicationsRead More
ZDI-25-950: 7-Zip ZIP File Parsing Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of 7-Zip. Interaction with this product is required to exploit this vulnerability but attack vectors may vary depending on the implementation. The ZDI has assigned a CVSS rating of 7.0. The following CVEs are assigned: CVE-2025-11002.
ZDI-25-949: 7-Zip ZIP File Parsing Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of 7-Zip. Interaction with this product is required to exploit this vulnerability but attack vectors may vary depending on the implementation. The ZDI has assigned a CVSS rating of 7.0. The following CVEs are assigned: CVE-2025-11001.
ZDI-25-948: Jaspersoft Jasper Reports JRLoader Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Jaspersoft Jasper Reports. Interaction with this library is required to exploit this vulnerability but attack vectors may vary depending on the implementation. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2025-10492.
ZDI-25-947: (0Day) Ivanti Endpoint Manager AgentPortal Deserialization of Untrusted Data Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Ivanti Endpoint Manager. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8.
ZDI-25-933: (Pwn2Own) Redis Lua Use-After-Free Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Redis. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2025-49844.
ZDI-25-932: MLflow Weak Password Requirements Authentication Bypass Vulnerability
This vulnerability allows remote attackers to bypass authentication on affected installations of MLflow. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.1. The following CVEs are assigned: CVE-2025-11200.
ZDI-25-931: MLflow Tracking Server Model Creation Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of MLflow Tracking Server. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.1. The following CVEs are assigned: CVE-2025-11201.
ZDI-25-930: win-cli-mcp-server resolveCommandPath Command Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of win-cli-mcp-server. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2025-11202.






