


Month: August 2025
ZDI-25-843: (Pwn2Own) Microsoft Windows win32kbase Type Confusion Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Microsoft Windows. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2025-50168.
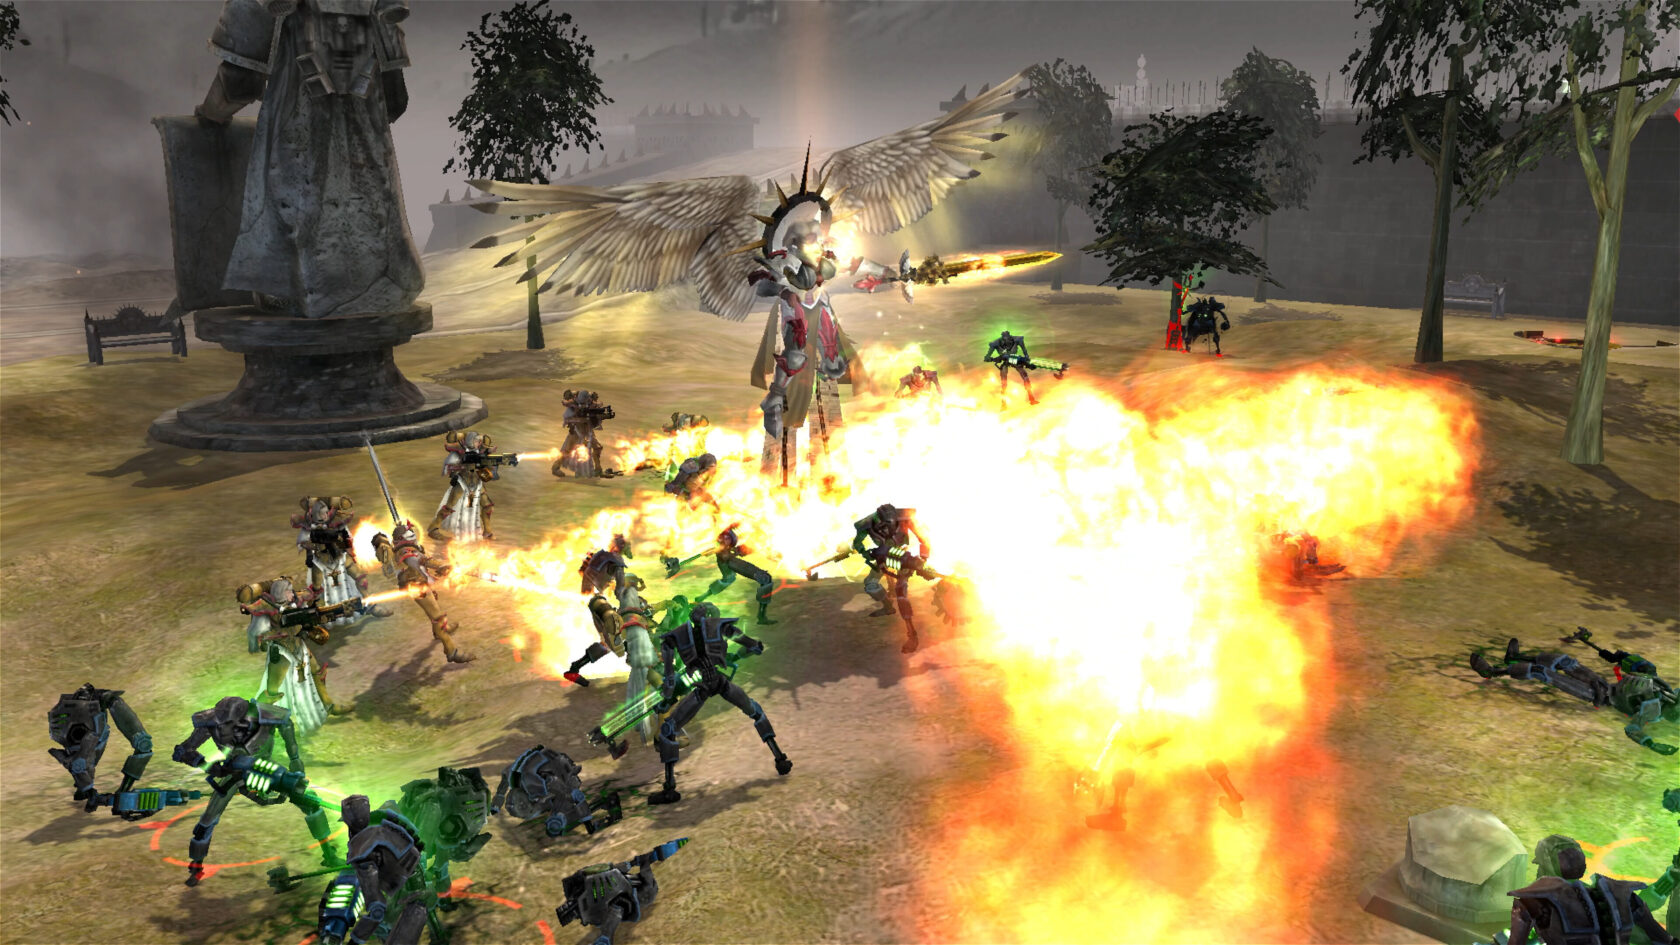
‘Warhammer 40,000: Dawn of War – Definitive Edition’ Storms GeForce NOW at Launch
Warhammer 40,000: Dawn of War – Definitive Edition is marching onto GeForce NOW, expanding the cloud gaming platform’s library to over 2,300 supported titles. Battle is just a click away, as the iconic real-time strategy game joins seven new releases this week. Commanders can prepare their squads and steel their nerves on any device — …
‘Warhammer 40,000: Dawn of War – Definitive Edition’ Storms GeForce NOW at LaunchRead More
NVIDIA, National Science Foundation Support Ai2 Development of Open AI Models to Drive U.S. Scientific Leadership
NVIDIA is partnering with the U.S. National Science Foundation (NSF) to create an AI system that supports the development of multimodal language models for advancing scientific research in the United States. The partnership supports the NSF Mid-Scale Research Infrastructure project, called Open Multimodal AI Infrastructure to Accelerate Science (OMAI). “Bringing AI into scientific research has …
ZDI-25-837: Rockwell Automation Arena Simulation DOE File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Rockwell Automation Arena Simulation. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-6377.
ZDI-25-836: Rockwell Automation Arena Simulation DOE File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Rockwell Automation Arena Simulation. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-6376.
ZDI-25-835: NoMachine Uncontrolled Search Path Element Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of NoMachine. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-8614.
ZDI-25-834: Academy Software Foundation OpenEXR EXR File Parsing Heap-based Buffer Overflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Academy Software Foundation OpenEXR. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2025-48071.
ZDI-25-830: (0Day) Schneider Electric EcoStruxure Power Monitoring Expert GetPagesAsImages Server-Side Request Forgery Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Schneider Electric EcoStruxure Power Monitoring Expert. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.5. The following CVEs are assigned: CVE-2025-54924.
ZDI-25-829: (0Day) Schneider Electric EcoStruxure Power Monitoring Expert GetFilteredSinkProvider Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Schneider Electric EcoStruxure Power Monitoring Expert. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2025-54923.
ZDI-25-828: (0Day) Schneider Electric EcoStruxure Power Monitoring Expert HttpPostedFile Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Schneider Electric EcoStruxure Power Monitoring Expert. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2025-54927.






