


Year: 2024
ZDI-24-424: Adobe Acrobat Reader DC AcroForm Use-After-Free Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Adobe Acrobat Reader DC. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-30305.
NVIDIA DGX SuperPOD to Power US Government Generative AI
In support of President Biden’s executive order on AI, the U.S. government will use an NVIDIA DGX SuperPOD to produce generative AI advances in climate science, healthcare and cybersecurity. The executive order, issued in October, is aimed at ensuring U.S. leadership in AI and managing its risks. MITRE, a nonprofit organization that operates federally funded …
NVIDIA DGX SuperPOD to Power US Government Generative AIRead More
A Mighty Meeting: Generative AI, Cybersecurity Connect at RSA
Cybersecurity experts at the RSA Conference this week will be on the hunt for ways to secure their operations in the era of generative AI. They’ll find many of the latest tools use AI and accelerated computing. This intersection of security and AI is coming into focus with collaborations that companies like NVIDIA and its …
A Mighty Meeting: Generative AI, Cybersecurity Connect at RSARead More
NVIDIA and Alphabet’s Intrinsic Put Next-Gen Robotics Within Grasp
Intrinsic, a software and AI robotics company at Alphabet, has integrated NVIDIA AI and Isaac platform technologies to advance the complex field of autonomous robotic manipulation. This week at the Automate trade show, in Chicago, Intrinsic is spotlighting leaps in robotic grasping and industrial scalability assisted by foundation models enabled by NVIDIA Isaac Manipulator, unlocking …
NVIDIA and Alphabet’s Intrinsic Put Next-Gen Robotics Within GraspRead More
CVE-2024-2887: A Pwn2Own Winning Bug in Google Chrome
In this guest blog from Master of Pwn winner Manfred Paul, he details CVE-2024-2887 – a type confusion bug that occurs in both Google Chrome and Microsoft Edge (Chromium). He used this bug as a part of his winning exploit that led to code execution in the renderer of both browsers. This bug was quickly …
CVE-2024-2887: A Pwn2Own Winning Bug in Google ChromeRead More
NVIDIA AI Microservices for Drug Discovery, Digital Health Now Integrated With AWS
Harnessing optimized AI models for healthcare is easier than ever as NVIDIA NIM, a collection of cloud-native microservices, integrates with Amazon Web Services. NIM, part of the NVIDIA AI Enterprise software platform available on AWS Marketplace, enables developers to access a growing library of AI models through industry-standard application programming interfaces, or APIs. The library …
NVIDIA AI Microservices for Drug Discovery, Digital Health Now Integrated With AWSRead More
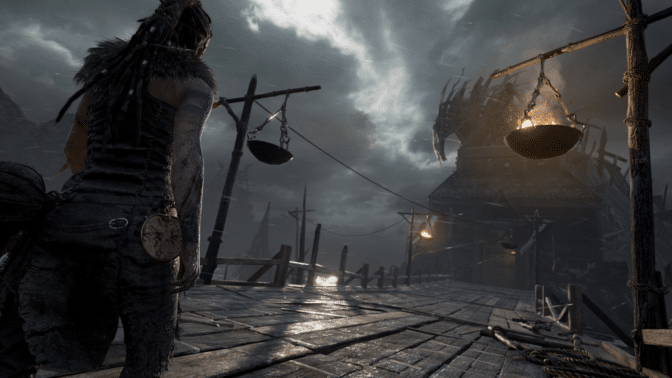
GeForce NOW Delivers 24 A-May-zing Games This Month
GeForce NOW brings 24 new games for members this month. Ninja Theory’s highly anticipated Senua’s Saga: Hellblade II will be coming to the cloud soon — get ready by streaming the first in the series, Hellblade: Senua’s Sacrifice, part of the seven new games joining the GeForce NOW library this week. Plus, game across more …
GeForce NOW Delivers 24 A-May-zing Games This MonthRead More
ZDI-24-419: (Pwn2Own) Xiaomi Pro 13 GetApps integral-dialog-page Cross-Site Scripting Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Xiaomi Pro 13 smartphones. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-4406.
ZDI-24-418: (Pwn2Own) Xiaomi Pro 13 mimarket manual-upgrade Cross-Site Scripting Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Xiaomi Pro 13 smartphones. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-4405.
ZDI-24-417: Xiaomi Pro 13 isUrlMatchLevel Permissive List of Allowed Inputs Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Xiaomi Pro 13 smartphones. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2023-26322.






