


Year: 2024
ZDI-24-559: G DATA Total Security Link Following Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of G DATA Total Security. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-1867.
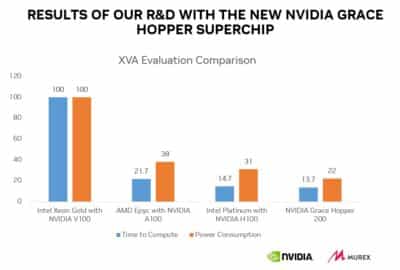
NVIDIA Grace Hopper Superchip Accelerates Murex MX.3 Analytics Performance, Reduces Power Consumption
After the 2008 financial crisis and increased risk-management regulations that followed, Pierre Spatz anticipated banks would focus on reducing computing expenses. As head of quantitative research at Murex, a trading and risk management software company based in Paris, Spatz adopted NVIDIA’s CUDA and GPU-accelerated computing, aiming for top performance and energy efficiency. Always seeking the …
ZDI-24-526: (Pwn2Own) VMware Workstation VBluetoothHCI_PacketOut Use-After-Free Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of VMware Workstation. An attacker must first obtain the ability to execute high-privileged code on the target guest system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.2. The following CVEs are assigned: CVE-2024-22267.
CVE-2024-30043: Abusing URL Parsing Confusion to Exploit XXE on SharePoint Server and Cloud
Yes, the title is right. This blog covers an XML eXternal Entity (XXE) injection vulnerability that I found in SharePoint. The bug was recently patched by Microsoft. In general, XXE vulnerabilities are not very exciting in terms of discovery and related technical aspects. They may sometimes be fun to exploit and exfiltrate data (or do …
CVE-2024-30043: Abusing URL Parsing Confusion to Exploit XXE on SharePoint Server and CloudRead More
Elevate Your Expertise: NVIDIA Introduces AI Infrastructure and Operations Training and Certification
NVIDIA has introduced a self-paced course, called AI Infrastructure and Operations Fundamentals, to provide enterprise professionals with essential training on the infrastructure and operational aspects of AI and accelerated computing. From enhancing speech recognition systems to powering self-driving cars, AI is transforming everyday life. The new course explains how to deploy and manage scalable infrastructure …
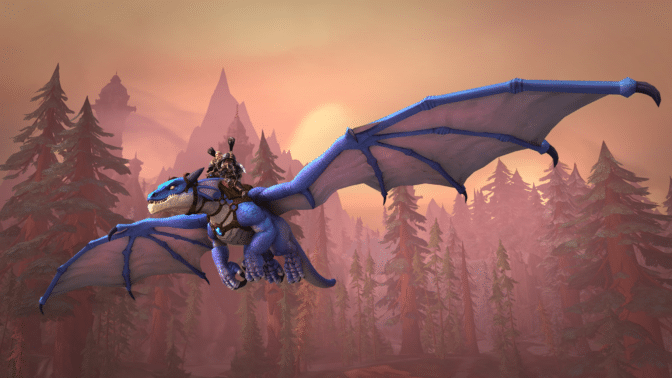
GeForce NOW Brings the Heat With ‘World of Warcraft’
World of Warcraft comes to the cloud this week, part of the 17 games joining the GeForce NOW library, with seven available to stream this week. Plus, it’s time to get rewarded. Get a free in-game mount in Elder Scrolls Online starting today by opting into GeForce NOW’s Rewards program. Heroes Rise to the Cloud …
GeForce NOW Brings the Heat With ‘World of Warcraft’Read More
ZDI-24-525: A10 Thunder ADC Incorrect Permission Assignment Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of A10 Thunder ADC. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-30369.
ZDI-24-524: A10 Thunder ADC CsrRequestView Command Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of A10 Thunder ADC. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2024-30368.
ZDI-24-523: Phoenix Contact CHARX SEC-3100 Link Following Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Phoenix Contact CHARX SEC-3100 charging controllers. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-28137.
ZDI-24-522: (Pwn2Own) Phoenix Contact CHARX SEC-3100 Filename Command Injection Remote Code Execution Vulnerability
This vulnerability allows network-adjacent attackers to execute arbitrary code on affected installations of Phoenix Contact CHARX SEC-3100 devices. Although authentication is required to exploit this vulnerability, the existing authentication mechanism can be bypassed. The ZDI has assigned a CVSS rating of 6.8. The following CVEs are assigned: CVE-2024-28135.






