


Year: 2024
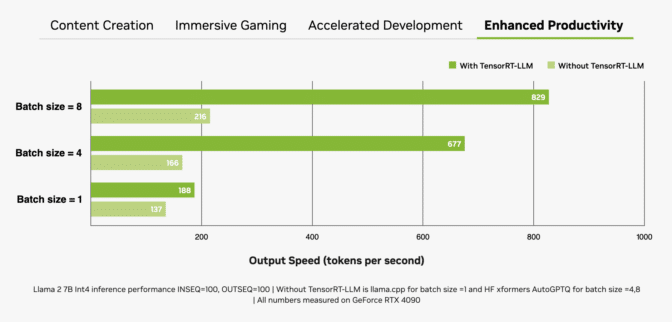
TOPS of the Class: Decoding AI Performance on RTX AI PCs and Workstations
Editor’s note: This post is part of the AI Decoded series, which demystifies AI by making the technology more accessible, and showcases new hardware, software, tools and accelerations for RTX PC users. The era of the AI PC is here, and it’s powered by NVIDIA RTX and GeForce RTX technologies. With it comes a new …
TOPS of the Class: Decoding AI Performance on RTX AI PCs and WorkstationsRead More
ZDI-24-600: Schneider Electric APC Easy UPS Online startRun Exposed Dangerous Method Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Schneider Electric APC Easy UPS Online. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8.
ZDI-24-599: Adobe Substance 3D Stager SKP File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Adobe Substance 3D Stager. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-34115.
ZDI-24-598: (0Day) Microsoft Windows Incorrect Permission Assignment Information Disclosure Vulnerability
This vulnerability allows local attackers to disclose sensitive information or to create a denial-of-service condition on affected installations of Microsoft Windows. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. Furthermore, the vulnerable behavior occurs only in certain hardware configurations. The ZDI has …
The June 2024 Security Update Review
Somehow, we’ve made it to the sixth patch Tuesday of 2024, and Microsoft and Adobe have released their regularly scheduled updates. Take a break from your regular activities and join us as we review the details of their latest security alerts. If you’d rather watch the full video recap covering the entire release, you can …
ZDI-24-597: Centreon initCurveList SQL Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Centreon. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-5725.
ZDI-24-596: Centreon updateServiceHost_MC SQL Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Centreon. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-32501.
ZDI-24-595: Centreon updateServiceHost SQL Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Centreon. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-5723.
ZDI-24-594: Siemens Tecnomatix Plant Simulation MODEL File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Siemens Tecnomatix Plant Simulation. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-32639.
Why Accelerated Data Processing Is Crucial for AI Innovation in Every Industry
Across industries, AI is supercharging innovation with machine-powered computation. In finance, bankers are using AI to detect fraud more quickly and keep accounts safe, telecommunications providers are improving networks to deliver superior service, scientists are developing novel treatments for rare diseases, utility companies are building cleaner, more reliable energy grids and automotive companies are making …
Why Accelerated Data Processing Is Crucial for AI Innovation in Every IndustryRead More






