


Year: 2024
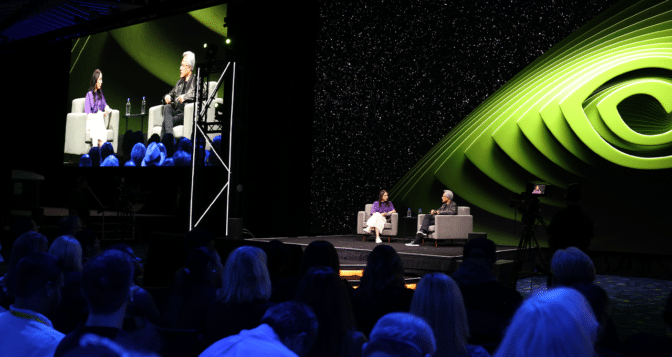
‘Everybody Will Have an AI Assistant,’ NVIDIA CEO Tells SIGGRAPH Audience
The generative AI revolution — with deep roots in visual computing — is amplifying human creativity even as accelerated computing promises significant gains in energy efficiency, NVIDIA founder and CEO Jensen Huang said Monday. That makes this week’s SIGGRAPH professional graphics conference, in Denver, the logical venue to discuss what’s next. “Everybody will have an …
‘Everybody Will Have an AI Assistant,’ NVIDIA CEO Tells SIGGRAPH AudienceRead More
ZDI-24-974: IrfanView CIN File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of IrfanView. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-6822.
ZDI-24-973: IrfanView CIN File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of IrfanView. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-6821.
ZDI-24-972: IrfanView AWD File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of IrfanView. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-6820.
ZDI-24-971: IrfanView PSP File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of IrfanView. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-6819.
ZDI-24-966: Docker Desktop Daemon CLI External Control of File Path Denial-of-Service Vulnerability
This vulnerability allows local attackers to create a denial-of-service condition on affected installations of Docker Desktop. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 6.1. The following CVEs are assigned: CVE-2024-5652.
ZDI-24-965: Apple macOS VideoToolbox Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Apple macOS. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-27829.
ZDI-24-964: Autodesk AutoCAD STEP File Parsing Memory Corruption Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Autodesk AutoCAD. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-23147.
ZDI-24-963: Autodesk AutoCAD X_T File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Autodesk AutoCAD. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-23146.
ZDI-24-962: Autodesk AutoCAD X_T File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Autodesk AutoCAD. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-23146.






