


Year: 2024
ZDI-24-1310: Lenovo Service Bridge Command Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Lenovo Service Bridge. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.5. The following CVEs are assigned: CVE-2024-4696.
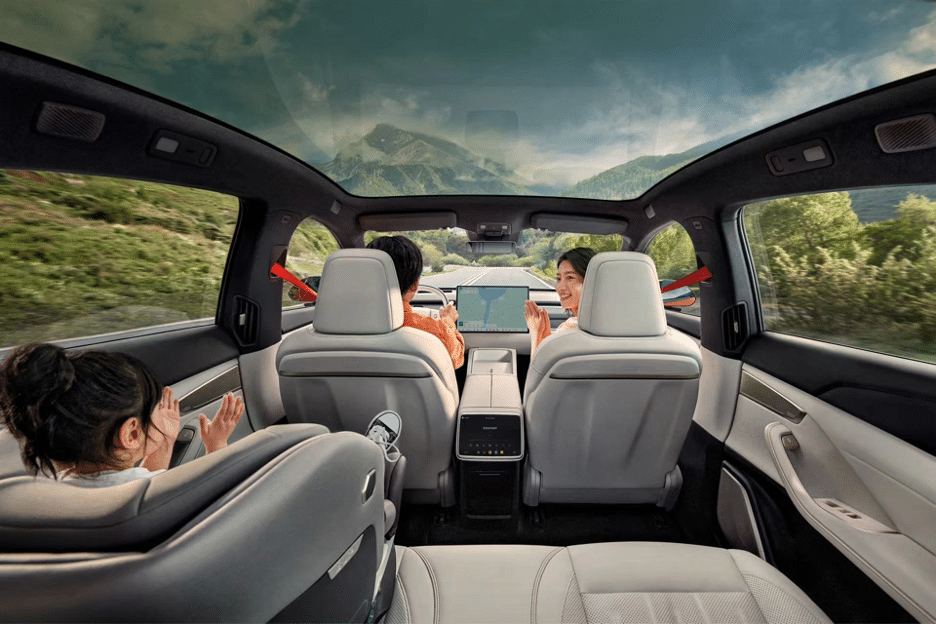
Bon Voyage: NIO Unveils ONVO L60 Smart Electric SUV, Built on NVIDIA DRIVE Orin
NIO’s smart EV brand, ONVO, has unveiled the L60 flagship mid-size family SUV, built on the NVIDIA DRIVE Orin system-on-a-chip. Earlier this year, the automaker introduced the ONVO brand — which stands for On Voyage — to reinforce its commitment to bringing safer, smarter, and more enjoyable and affordable mobility solutions for the mainstream family …
Bon Voyage: NIO Unveils ONVO L60 Smart Electric SUV, Built on NVIDIA DRIVE OrinRead More
ZDI-24-1309: Foxit PDF Reader AcroForm Out-Of-Bounds Read Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Foxit PDF Reader. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 3.3. The following CVEs are assigned: CVE-2024-9256.
ZDI-24-1308: Foxit PDF Reader Annotation Use-After-Free Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Foxit PDF Reader. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-9255.
ZDI-24-1307: Foxit PDF Reader Annotation Use-After-Free Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Foxit PDF Reader. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-9254.
ZDI-24-1306: Foxit PDF Reader Annotation Use-After-Free Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Foxit PDF Reader. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 3.3. The following CVEs are assigned: CVE-2024-9251.
Exploiting Exchange PowerShell After ProxyNotShell: Part 4 – No Argument Constructor
As you may know, I recently presented my Exchange-related talk during OffensiveCon 2024. This series of 4 blog posts is meant to supplement the talk and provide additional technical details. In this final part, I ’am going to describe the PowerShell Remoting ConvertViaNoArgumentConstructor conversion mechanism, which I underestimated at the beginning of my research. It …
Exploiting Exchange PowerShell After ProxyNotShell: Part 4 – No Argument ConstructorRead More
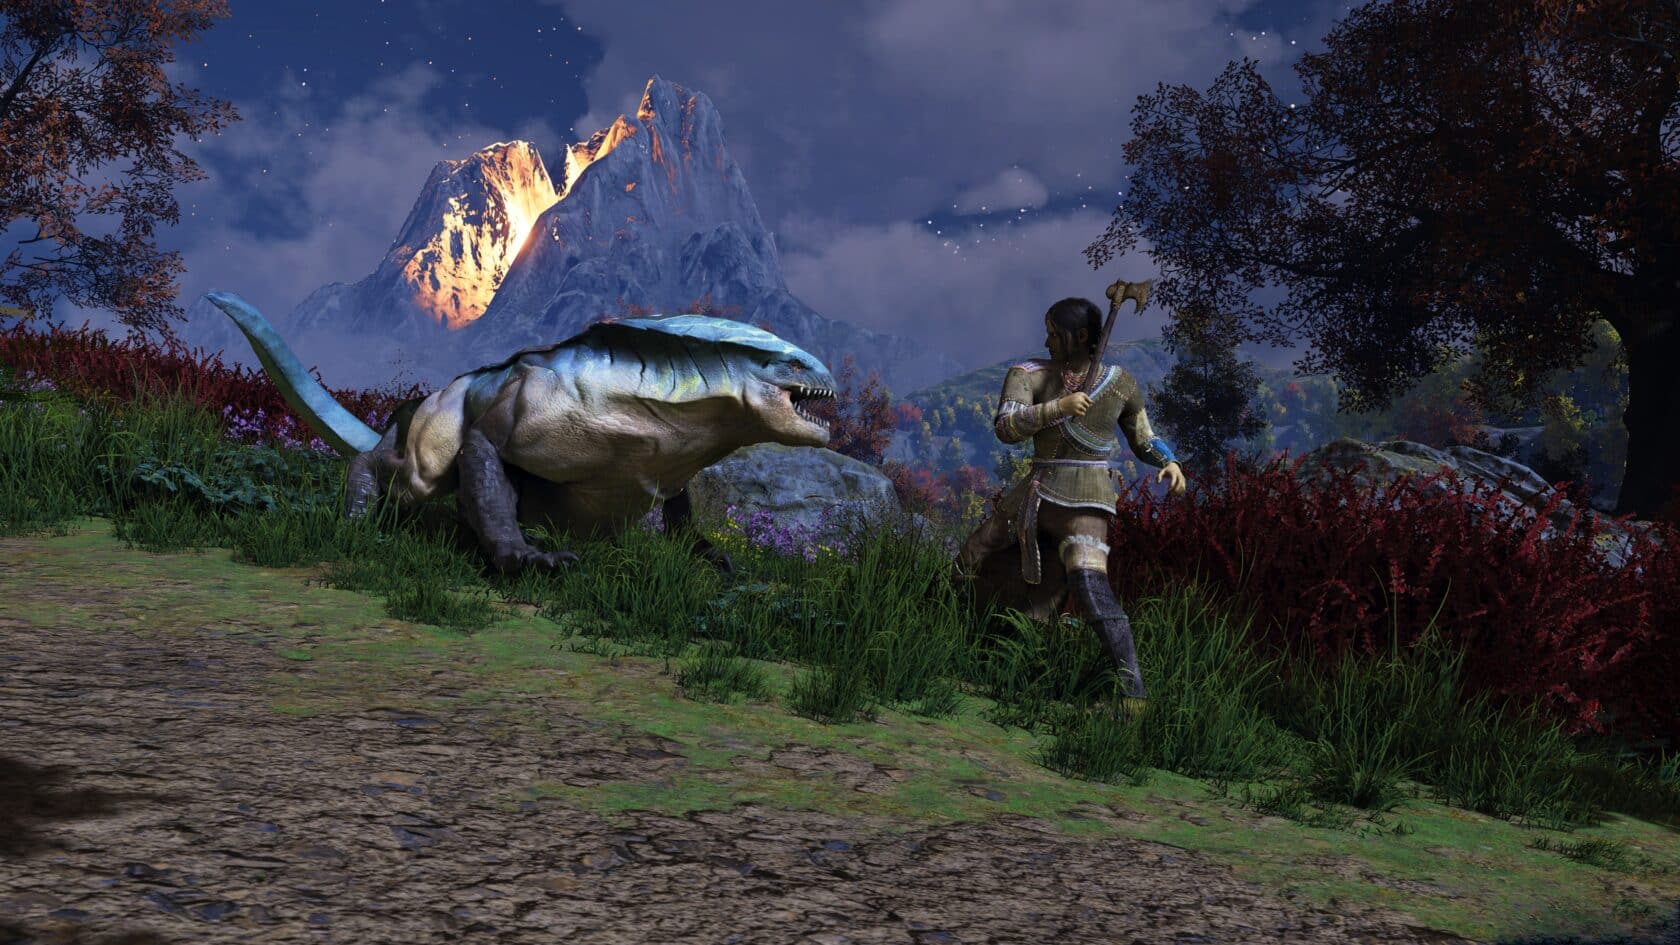
A Whole New World: ‘GreedFall II: The Dying World’ Joins GeForce NOW
Whether looking for a time-traveling adventure, strategic roleplay or epic action, anyone can find something to play on GeForce NOW, with over 2,000 games in the cloud. The GeForce NOW library continues to grow with seven titles arriving this week, including the role-playing game GreedFall II: The Dying World from developer Spiders and publisher Nacon. …
A Whole New World: ‘GreedFall II: The Dying World’ Joins GeForce NOWRead More
ZDI-24-1288: Apple macOS AppleIntelKBLGraphicsMTLDriver Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Apple macOS. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.5. The following CVEs are assigned: CVE-2024-40846.
ZDI-24-1287: Apple macOS AppleVADriver Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Apple macOS. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-44160.






