


Year: 2024
ZDI-24-1511: Microsoft Office PowerPoint PPTX File Parsing Use-After-Free Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Microsoft Office PowerPoint. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-49032.
Open for Development: NVIDIA Works With Cloud-Native Community to Advance AI and ML
Cloud-native technologies have become crucial for developers to create and implement scalable applications in dynamic cloud environments. This week at KubeCon + CloudNativeCon North America 2024, one of the most-attended conferences focused on open-source technologies, Chris Lamb, vice president of computing software platforms at NVIDIA, delivered a keynote outlining the benefits of open source for …
Open for Development: NVIDIA Works With Cloud-Native Community to Advance AI and MLRead More
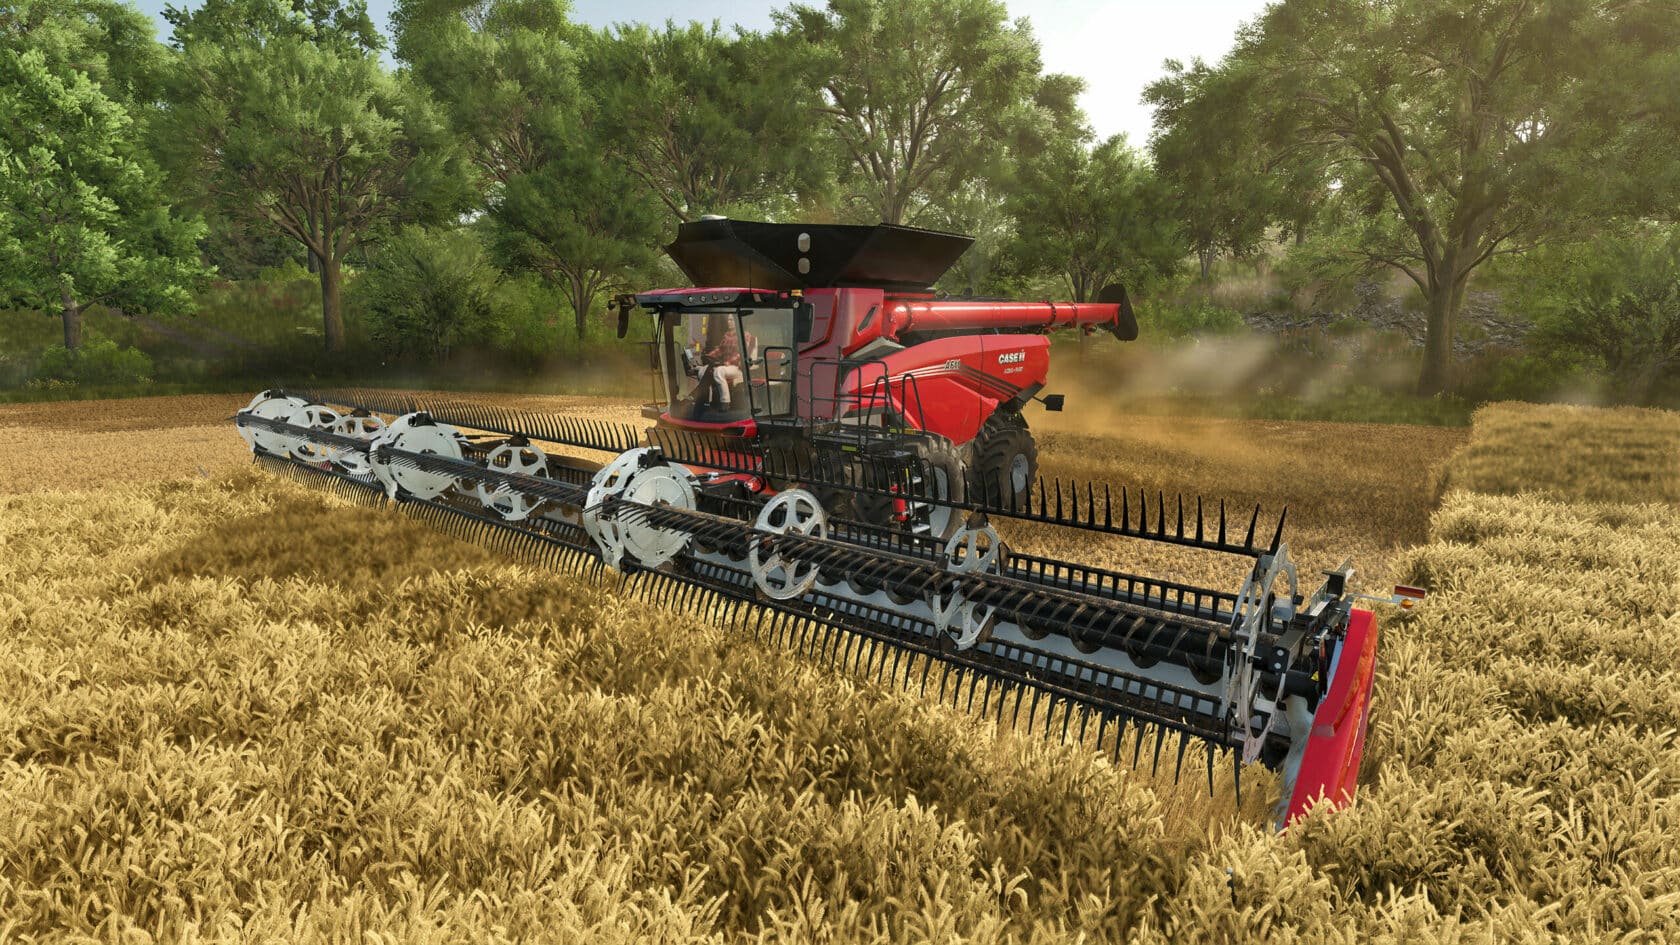
From Seed to Stream: ‘Farming Simulator 25’ Sprouts on GeForce NOW
Grab a pitchfork and fire up the tractor — the fields of GeForce NOW are about to get a whole lot greener with Farming Simulator 25. Whether looking for a time-traveling adventure, cozy games or epic action, GeForce NOW has something for everyone with over 2,000 games in its cloud library. Nine titles arrive this …
From Seed to Stream: ‘Farming Simulator 25’ Sprouts on GeForce NOWRead More
ZDI-24-1510: Ivanti Endpoint Manager GetComputerID SQL Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ivanti Endpoint Manager. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2024-50330.
ZDI-24-1509: Ivanti Endpoint Manager vulscan Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ivanti Endpoint Manager. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-50329.
ZDI-24-1508: Ivanti Endpoint Manager GetDetectedVulnerabilitiesDataTable SQL Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ivanti Endpoint Manager. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2024-50328.
ZDI-24-1507: Ivanti Endpoint Manager ROI SQL Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ivanti Endpoint Manager. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2024-50327.
2025 Predictions: AI Finds a Reason to Tap Industry Data Lakes
Since the advent of the computer age, industries have been so awash in stored data that most of it never gets put to use. This data is estimated to be in the neighborhood of 120 zettabytes — the equivalent of trillions of terabytes, or more than 120x the amount of every grain of sand on …
2025 Predictions: AI Finds a Reason to Tap Industry Data LakesRead More
Peak Training: Blackwell Delivers Next-Level MLPerf Training Performance
Generative AI applications that use text, computer code, protein chains, summaries, video and even 3D graphics require data-center-scale accelerated computing to efficiently train the large language models (LLMs) that power them. In MLPerf Training 4.1 industry benchmarks, the NVIDIA Blackwell platform delivered impressive results on workloads across all tests — and up to 2.2x more …
Peak Training: Blackwell Delivers Next-Level MLPerf Training PerformanceRead More
ZDI-24-1486: (0Day) G DATA Total Security Incorrect Permission Assignment Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of G DATA Total Security. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.0. The following CVEs are assigned: CVE-2024-6871.






