


Month: December 2024
Tech Leader, AI Visionary, Endlessly Curious Jensen Huang to Keynote CES 2025
On Jan. 6 at 6:30 p.m. PT, NVIDIA founder and CEO Jensen Huang — with his trademark leather jacket and an unwavering vision — will step onto the CES 2025 stage. From humble beginnings as a busboy at a Denny’s to founding NVIDIA, Huang’s story embodies innovation and perseverance. Huang has been named the world’s …
Tech Leader, AI Visionary, Endlessly Curious Jensen Huang to Keynote CES 2025Read More
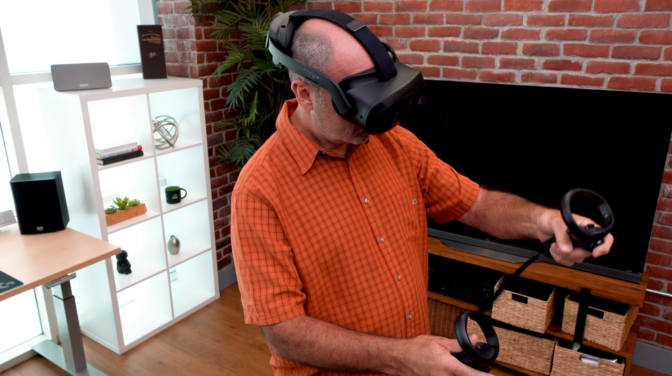
What Is Extended Reality?
Editor’s note: This article, originally published on May 20, 2022, has been updated. Advances in extended reality have already changed the way we work, live and play, and it’s just getting started. Extended reality, or XR, is an umbrella category that covers a spectrum of newer, immersive technologies, including virtual reality, augmented reality and mixed …
ZDI-24-1688: Linux Kernel ksmbd PreviousSessionId Race Condition Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Linux Kernel. Authentication is required to exploit this vulnerability. However, only systems with ksmbd enabled are vulnerable. The ZDI has assigned a CVSS rating of 8.5.
ZDI-24-1687: Progress Software WhatsUp Gold GetFilterCriteria SQL Injection Privilege Escalation Vulnerability
This vulnerability allows remote attackers to escalate privileges on affected installations of Progress Software WhatsUp Gold. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-46908.
ZDI-24-1686: Progress Software WhatsUp Gold GetFilterCriteria SQL Injection Privilege Escalation Vulnerability
This vulnerability allows remote attackers to escalate privileges on affected installations of Progress Software WhatsUp Gold. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-46907.
ZDI-24-1685: Progress Software WhatsUp Gold GetOrderByClause SQL Injection Privilege Escalation Vulnerability
This vulnerability allows remote attackers to escalate privileges on affected installations of Progress Software WhatsUp Gold. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-46905.
SolarWinds Access Rights Manager: One Vulnerability to LPE Them All
Some time ago, I spent some time researching a core SolarWinds product, SolarWinds Platform (previously Orion Platform). At that time, I hadn’t been aware of the SolarWinds Access Right Manager product (Solar Winds ARM). Afterward, Trend Micro’s Zero Day Initiative began receiving submissions of vulnerabilities in Access Rights Manager (ARM). The first submissions we received …
SolarWinds Access Rights Manager: One Vulnerability to LPE Them AllRead More
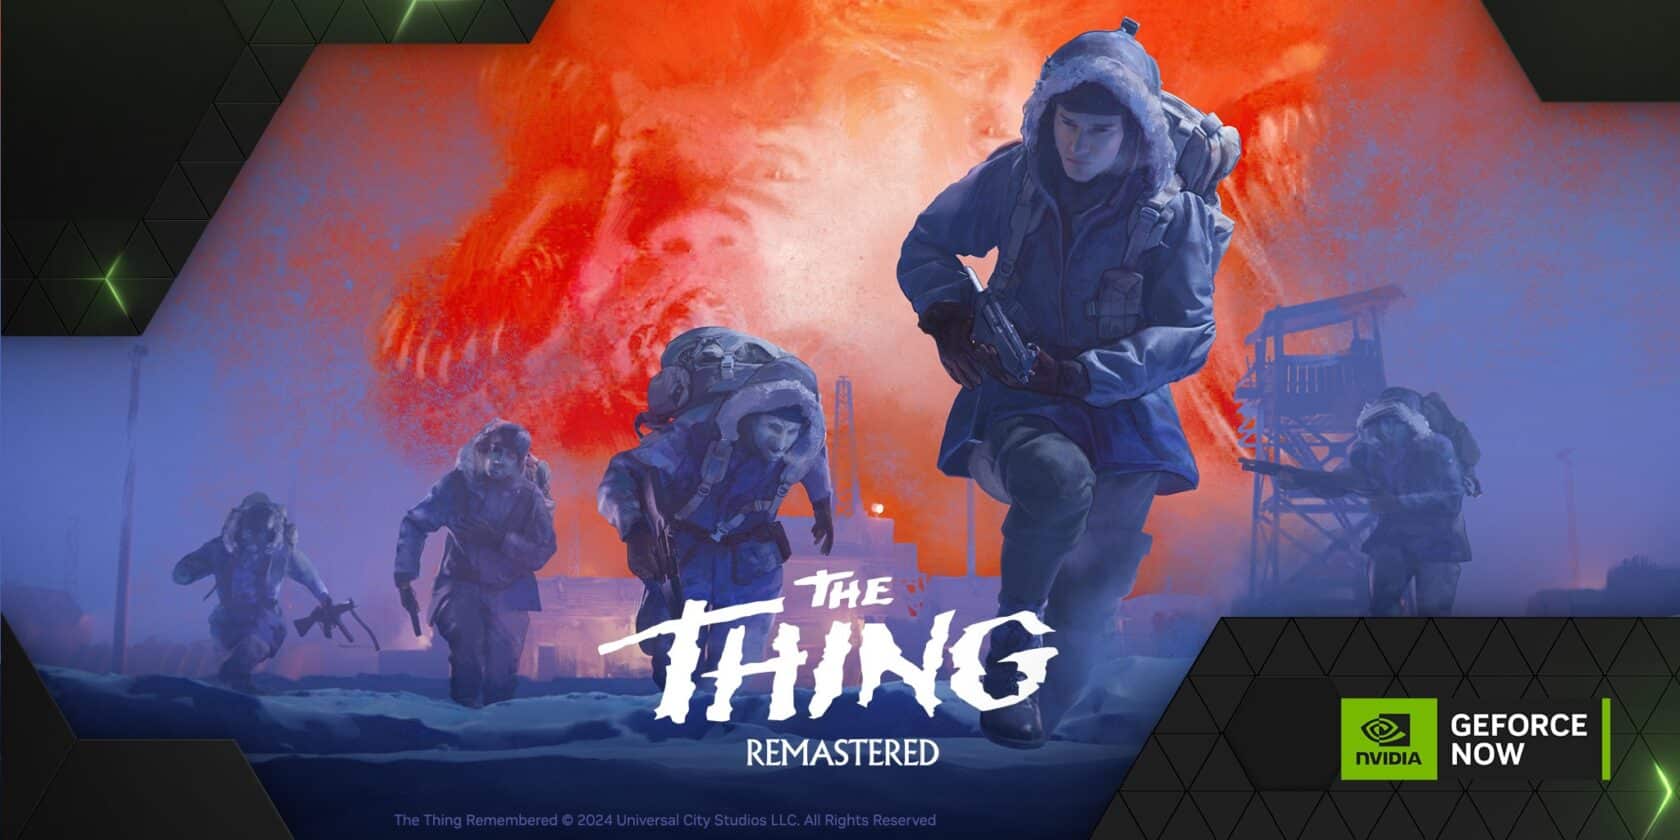
Ready Player Fun: GFN Thursday Brings Six New Adventures to the Cloud
From heart-pounding action games to remastered classics, there’s something for everyone this GFN Thursday. Six new titles join the cloud this week, starting with The Thing: Remastered. Face the horrors of the Antarctic as the game oozes onto GeForce NOW. Nightdive Studios’ revival of the cult-classic 2002 survival-horror game came to the cloud as a …
Ready Player Fun: GFN Thursday Brings Six New Adventures to the CloudRead More
ZDI-24-1681: Tungsten Automation Power PDF JPF File Parsing Out-Of-Bounds Write Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Tungsten Automation Power PDF. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-12547.
ZDI-24-1680: Tungsten Automation Power PDF JP2 File Parsing Use-After-Free Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Tungsten Automation Power PDF. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 3.3. The following CVEs are assigned: CVE-2024-12548.






