


Month: September 2024
Upgrade Livestreams With Twitch Enhanced Broadcasting and NVIDIA Encoder
At TwitchCon — a global convention for the Twitch livestreaming platform—livestreamers and content creators this week can experience the latest technologies for accelerating creative workflows and improving video quality. That includes the beta release of Twitch Enhanced Broadcasting support for HEVC when using the NVIDIA encoder. Content creators can also use the NVIDIA Broadcast app, …
Upgrade Livestreams With Twitch Enhanced Broadcasting and NVIDIA EncoderRead More
New AI Innovation Hub in Tunisia Drives Technological Advancement Across Africa
A new AI innovation hub for developers across Tunisia launched today in Novation City, a technology park that’s designed to cultivate a vibrant, innovation ecosystem in mechatronics — an industry encompassing IT, mechanics and electronics — and to foster synergy between education, research and industry in the North African country. Built in collaboration with the …
New AI Innovation Hub in Tunisia Drives Technological Advancement Across AfricaRead More
ZDI-24-1226: mySCADA myPRO Hard-Coded Credentials Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of mySCADA myPRO. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2024-4708.
ZDI-24-1225: SolarWinds Access Rights Manager Hard-Coded Credentials Authentication Bypass Vulnerability
This vulnerability allows remote attackers to bypass authentication on affected installations of SolarWinds Access Rights Manager. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.3. The following CVEs are assigned: CVE-2024-28990.
ZDI-24-1224: SolarWinds Access Rights Manager JsonSerializationBinder Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of SolarWinds Access Rights Manager. Although authentication is required to exploit this vulnerability, the existing authentication mechanism can be bypassed. The ZDI has assigned a CVSS rating of 9.9. The following CVEs are assigned: CVE-2024-28991.
ZDI-24-1223: Ivanti Endpoint Manager AgentPortal Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ivanti Endpoint Manager. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2024-29847.
Exploiting Exchange PowerShell After ProxyNotShell: Part 2 – ApprovedApplicationCollection
As you may know, I recently presented my Exchange-related talk during OffensiveCon 2024. This series of 4 blog posts is meant to supplement the talk and provide additional technical details. You can read the first post in this series here. In part 2, I describe the ApprovedApplicationCollection gadget, which was available for abuse because it …
Exploiting Exchange PowerShell After ProxyNotShell: Part 2 – ApprovedApplicationCollectionRead More
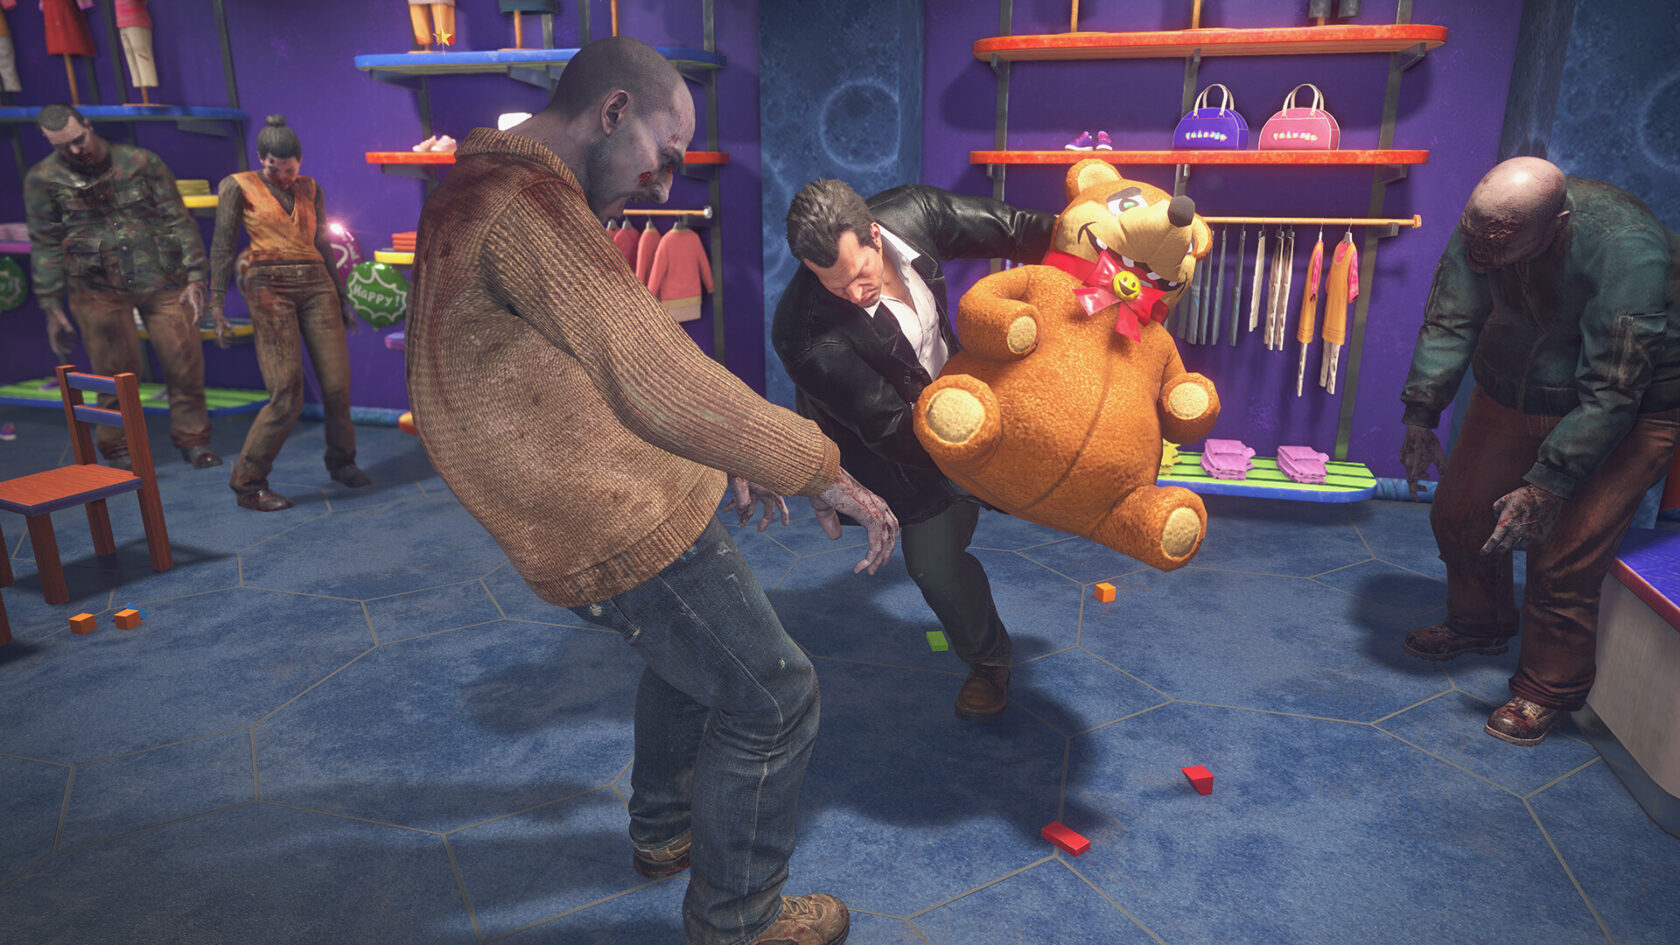
GeForce NOW to Bring ‘Dead Rising Deluxe Remaster’ to the Cloud at Launch
Rise and shine — Capcom’s latest action-adventure game, Dead Rising Deluxe Remaster, heads to the cloud at launch next week. It’s part of nine new titles joining the extensive GeForce NOW library. ‘Dead Rising’ Coming Soon From the ground to the cloud. Dead Rising Deluxe Remaster returns with modern graphics. More than just a remaster, …
GeForce NOW to Bring ‘Dead Rising Deluxe Remaster’ to the Cloud at LaunchRead More
ZDI-24-1222: Ivanti Workspace Control RES Exposed Dangerous Method Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Ivanti Workspace Control. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-8012.
ZDI-24-1221: Ivanti Endpoint Manager LoadMotherboardTable SQL Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ivanti Endpoint Manager. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.2. The following CVEs are assigned: CVE-2024-34785.






