


Day: September 13, 2024
ZDI-24-1223: Ivanti Endpoint Manager AgentPortal Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Ivanti Endpoint Manager. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8. The following CVEs are assigned: CVE-2024-29847.
Exploiting Exchange PowerShell After ProxyNotShell: Part 2 – ApprovedApplicationCollection
As you may know, I recently presented my Exchange-related talk during OffensiveCon 2024. This series of 4 blog posts is meant to supplement the talk and provide additional technical details. You can read the first post in this series here. In part 2, I describe the ApprovedApplicationCollection gadget, which was available for abuse because it …
Exploiting Exchange PowerShell After ProxyNotShell: Part 2 – ApprovedApplicationCollectionRead More
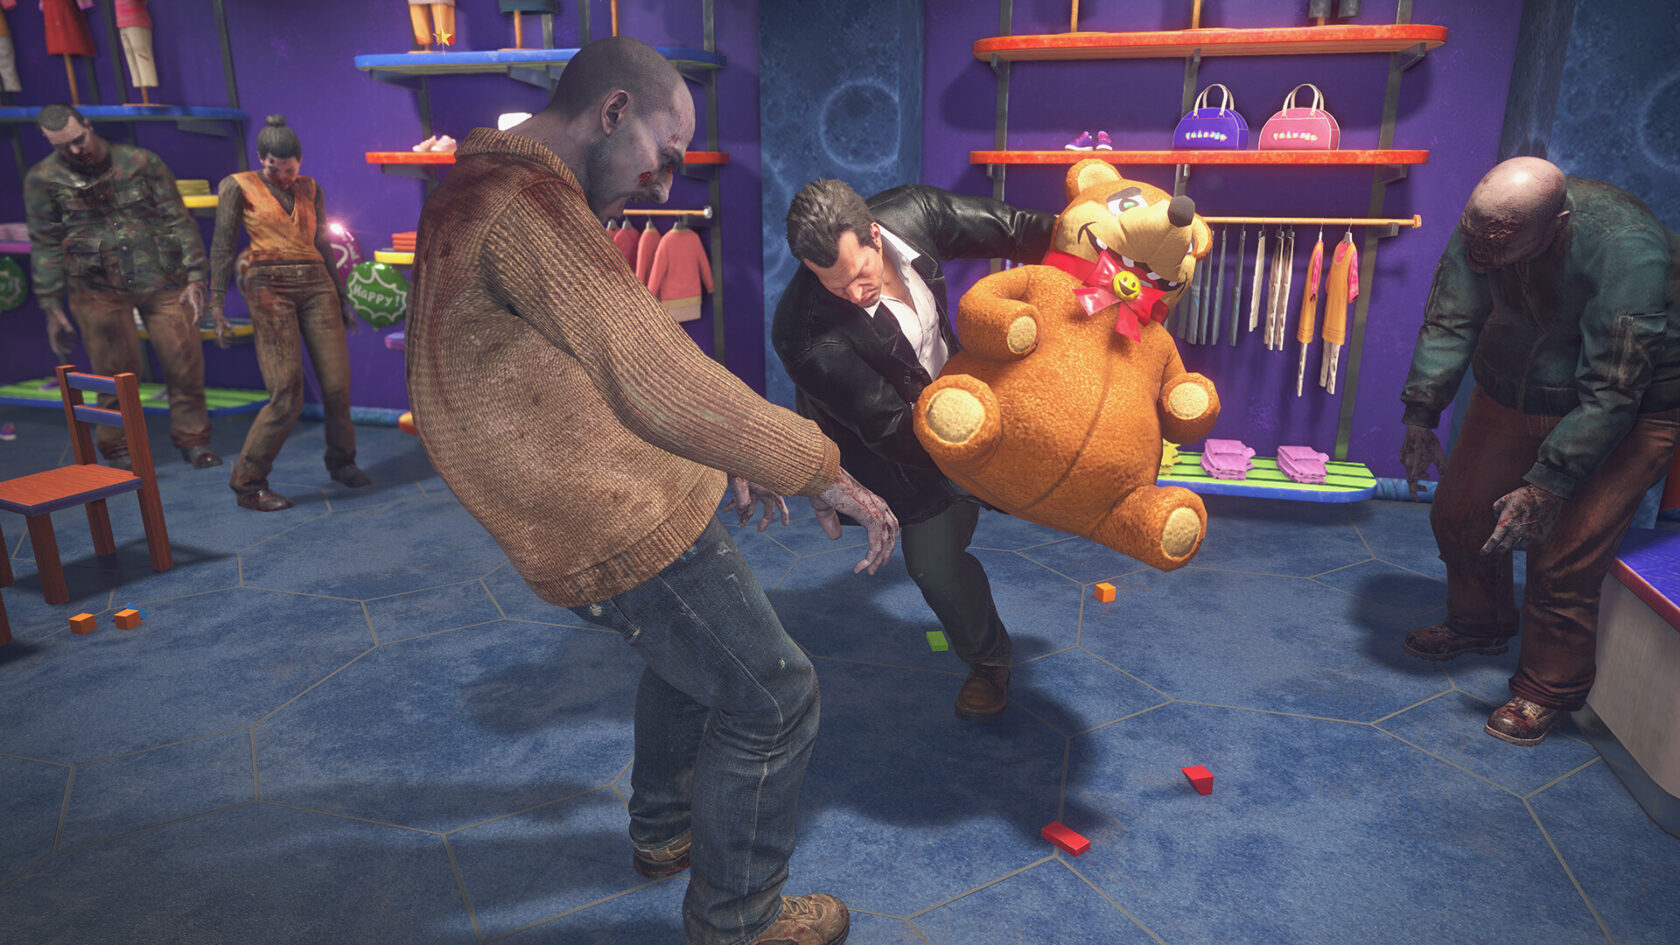
GeForce NOW to Bring ‘Dead Rising Deluxe Remaster’ to the Cloud at Launch
Rise and shine — Capcom’s latest action-adventure game, Dead Rising Deluxe Remaster, heads to the cloud at launch next week. It’s part of nine new titles joining the extensive GeForce NOW library. ‘Dead Rising’ Coming Soon From the ground to the cloud. Dead Rising Deluxe Remaster returns with modern graphics. More than just a remaster, …
GeForce NOW to Bring ‘Dead Rising Deluxe Remaster’ to the Cloud at LaunchRead More






