


Month: June 2024
ZDI-24-879: (Pwn2Own) Ubiquiti Networks EV Station changeUserPassword Missing Authentication Remote Code Execution Vulnerability
This vulnerability allows network-adjacent attackers to execute arbitrary code on affected installations of Ubiquiti Networks EV Station. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-29208.
ZDI-24-878: Sony XAV-AX5500 Insufficient Verification of Data Authenticity Remote Code Execution Vulnerability
This vulnerability allows physically present attackers to execute arbitrary code on affected installations of Sony XAV-AX5500 devices. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 6.8. The following CVEs are assigned: CVE-2024-23922.
ZDI-24-821: Linux Kernel TIPC Message Reassembly Use-After-Free Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Linux Kernel. Authentication is not required to exploit this vulnerability, but only systems with TIPC bearer enabled are vulnerable. The ZDI has assigned a CVSS rating of 9.0. The following CVEs are assigned: CVE-2024-36886.
ZDI-24-820: Windscribe Directory Traversal Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of Windscribe. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-6141.
ZDI-24-819: VIPRE Advanced Security Incorrect Permission Assignment Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of VIPRE Advanced Security. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-5930.
ZDI-24-818: VIPRE Advanced Security PMAgent Uncontrolled Search Path Element Local Privilege Escalation Vulnerability
This vulnerability allows local attackers to escalate privileges on affected installations of VIPRE Advanced Security. An attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-5929.
Crack the Case With ‘Tell Me Why’ and ‘As Dusk Falls’ on GeForce NOW
Sit back and settle in for some epic storytelling. Tell Me Why and As Dusk Falls — award-winning, narrative-driven games from Xbox Studios — add to the 1,900+ games in the GeForce NOW library, ready to stream from the cloud. Members can find more adventures with four new titles available this week. Experience a Metallica …
Crack the Case With ‘Tell Me Why’ and ‘As Dusk Falls’ on GeForce NOWRead More
Decoding How NVIDIA AI Workbench Powers App Development
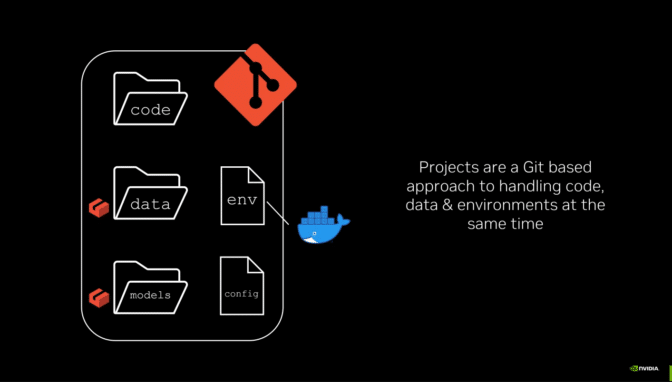
Editor’s note: This post is part of the AI Decoded series, which demystifies AI by making the technology more accessible and showcases new hardware, software, tools and accelerations for NVIDIA RTX PC and workstation users. The demand for tools to simplify and optimize generative AI development is skyrocketing. Applications based on retrieval-augmented generation (RAG) — …
Decoding How NVIDIA AI Workbench Powers App DevelopmentRead More
ZDI-24-815: Toshiba e-STUDIO2518A vsftpd Incorrect Permission Assignment Privilege Escalation Vulnerability
This vulnerability allows local attackers to execute arbitrary code on affected installations of Toshiba e-STUDIO2518A printers. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-3498.
ZDI-24-814: Toshiba e-STUDIO2518A unzip Directory Traversal Remote Code Execution Vulnerability
This vulnerability allows network-adjacent attackers to execute arbitrary code on affected installations of Toshiba e-STUDIO2518A printers. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 8.8. The following CVEs are assigned: CVE-2024-3497.






