


Month: April 2024
ZDI-24-401: Progress Software Telerik Reporting ObjectReader Deserialization of Untrusted Data Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Progress Software Telerik Reporting. User interaction is required to exploit this vulnerability in that the target must visit a malicious page or open a malicious file. The ZDI has assigned a CVSS rating of 7.8. The following CVEs are assigned: CVE-2024-1801.
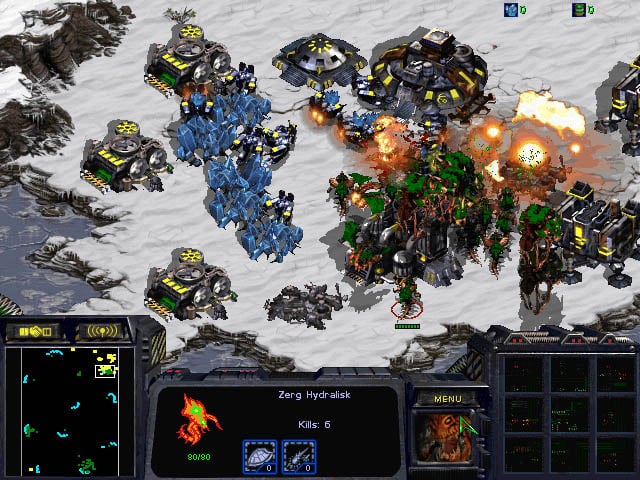
Blast From the Past: Stream ‘StarCraft’ and ‘Diablo’ on GeForce NOW
Support for Battle.net on GeForce NOW expands this GFN Thursday, as titles from the iconic StarCraft and Diablo series come to the cloud. StarCraft Remastered, StarCraft II, Diablo II: Resurrected and Diablo III are part of 16 new games joining the GeForce NOW library of more than 1,900 titles. Plus, a new update rolling out …
Blast From the Past: Stream ‘StarCraft’ and ‘Diablo’ on GeForce NOWRead More
Into the Omniverse: Unlocking the Future of Manufacturing With OpenUSD on Siemens Teamcenter X
Editor’s note: This post is part of Into the Omniverse, a series focused on how artists, developers and enterprises can transform their workflows using the latest advances in OpenUSD and NVIDIA Omniverse. Universal Scene Description, aka OpenUSD, is elevating the manufacturing game. Siemens, a leader in industrial technology, has embraced OpenUSD as a cornerstone of …
How Virtual Factories Are Making Industrial Digitalization a Reality
To address the shift to electric vehicles, increased semiconductor demand, manufacturing onshoring, and ambitions for greater sustainability, manufacturers are investing in new factory developments and re-engineering their existing facilities. These projects often run over budget and schedule, due to complex and manual planning processes, legacy technology infrastructure, and disconnected tools, data and teams. To address …
How Virtual Factories Are Making Industrial Digitalization a RealityRead More
NVIDIA to Acquire GPU Orchestration Software Provider Run:ai
To help customers make more efficient use of their AI computing resources, NVIDIA today announced it has entered into a definitive agreement to acquire Run:ai, a Kubernetes-based workload management and orchestration software provider. Customer AI deployments are becoming increasingly complex, with workloads distributed across cloud, edge and on-premises data center infrastructure. Managing and orchestrating generative …
NVIDIA to Acquire GPU Orchestration Software Provider Run:aiRead More
ZDI-24-396: Microsoft Azure ODSP nikisos Uncontrolled Search Path Element Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of ODSP for Microsoft Azure. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 9.8.
ZDI-24-395: Ivanti Avalanche WLInfoRailService DELKEY Directory Traversal Arbitrary File Deletion Vulnerability
This vulnerability allows remote attackers to delete arbitrary files on affected installations of Ivanti Avalanche. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.1. The following CVEs are assigned: CVE-2024-27984.
ZDI-24-394: Ivanti Avalanche WLAvalancheService Null Pointer Dereference Denial-of-Service Vulnerability
This vulnerability allows remote attackers to create a denial-of-service condition on affected installations of Ivanti Avalanche. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 6.5. The following CVEs are assigned: CVE-2024-27978.
ZDI-24-393: Ivanti Avalanche WLAvalancheService Directory Traversal Arbitrary File Deletion Vulnerability
This vulnerability allows remote attackers to delete arbitrary files on affected installations of Ivanti Avalanche. Authentication is required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 7.1. The following CVEs are assigned: CVE-2024-27977.
ZDI-24-369: Google cAdvisor REST API Improper Access Control Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of Google cAdvisor. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of 5.3.






